Chinese cyber espionage: a data leak reveals the secrets of their hackers

Unprecedented Data Leaks Expose Chinese Cyber Espionage Programs

Following an unprecedented data leak from a Beijing regime hacking service provider, the secrets of Chinese cyberespionage are revealed. The I-Soon company is said to have infiltrated dozens of strategic targets around the world. This is what you will discover here by reading this brief cyberculture. Unprecedented data leaks reveal China’s cyberespionage program.
Following an unprecedented data leak from a Beijing regime hacking service provider, the secrets of Chinese cyberespionage are revealed. Based on the analysis of this data, it appears that the I-Soon company has infiltrated dozens of strategic targets around the world. This is what you will discover here by reading this brief Cyberculture.

Stay informed with our posts dedicated to Cyberculture to track its evolution through our regularly updated topics.

[bws_pdfprint display=’print’]Read the secrets of Chinese cyber espionage revealed by an unprecedented data leak, written by Jacques Gascuel, a pioneer of contactless, serverless and databaseless sensitive data security solutions. Stay up to date and secure with our frequent updates..

Chinese cyber espionage I-Soon: A data leak reveals the secrets of their hackers

Chinese cyber espionage poses a serious threat to the security and stability of the world. Many countries and organizations face hackers who try to steal sensitive information, disrupt critical infrastructure, or influence political outcomes. One of the most active and sophisticated cyber espionage actors is China, which has a large and diverse hacking program. But how does China conduct its cyber operations? What methods, targets, and objectives does it have? And how can we protect ourselves from its attacks?

In this brief, we will explore these questions of Chinese cyber espionage, based on a recent data leak that revealed the inner workings of a Chinese cybersecurity vendor working for the Chinese government. The vendor, I-Soon, is a private contractor that operates as an advanced persistent threat (APT) for hire, serving the Chinese Ministry of Public Security (MPS). The leaked data, published on GitHub, contains hundreds of documents that document I-Soon’s Chinese cyber espionage activities, from staff complaints to hacking tools and services.

We will also look at some of the solutions that exist to counter the cyber espionage threat, both from a technical and a strategic perspective. We will focus on the solutions developed by Freemindtronic, an Andorran company that specializes in security and encryption technologies, based on the NFC HSM (Near Field Communication and Hardware Security Module) technology. We will also examine the means of counter espionage against the methods of I-Soon, which are varied and sophisticated.

I-Soon data leak reveals insight into Chinese cyber espionage hacking program

The I-Soon data leak is a significant revelation in Chinese cyber espionage, as it offers a rare glimpse into the inner workings of a major spyware and APT-for-hire provider. The leak exposes I-Soon’s methods, tools and goals, as well as the challenges and frustrations of its staff.

According to the leaked data, I-Soon infiltrated several government agencies, including those from India, Thailand, Vietnam, South Korea, and NATO. Some of the tools that I-Soon used are impressive. For example, they had a tool that could steal the user’s Twitter email and phone number, read personal messages, and publish tweets on the user’s behalf. They also had custom Remote Access Trojans (RATs) for Windows, iOS, and Android, that could perform various malicious actions, such as keylogging, file access logging, process management, and remote shell. They also had portable devices for attacking networks from the inside, and special equipment for operatives working abroad to establish safe communication.

The leak also reveals some of the challenges and difficulties that I-Soon faced, such as losing access to some of their data seized from government agencies, dealing with corrupt officials, and working in sensitive regions like Xinjiang. The leak also shows some of the internal complaints and grievances of I-Soon’s staff, such as low pay, poor management, and lack of recognition.

The leak is a treasure trove of intel for cybersecurity researchers and analysts, as it provides a rare insight into the day-to-day operations of China’s hacking program, which the FBI says is the biggest of any country. The leak also raises serious concerns for the security and sovereignty of the countries and organizations targeted by I-Soon, as it exposes the extent and the impact of China’s cyber espionage activities.

In summary, the I-Soon data leak exposed the secrets of Chinese cyber espionage, which poses a major challenge to world security and stability. Faced with this threat, it is necessary to strengthen cooperation and defense in cybersecurity, while respecting the principles of freedom and transparency on the internet. It is also important to understand China’s motivations and objectives, in order to find peaceful and lasting solutions.

Reactions and challenges to the Chinese cyber espionage threat

The revelation of the I-Soon data leak comes amid growing tensions between China and its rivals, notably the United States, which regularly accuses it of carrying out cyberattacks against their interests. China, for its part, denies any involvement and presents itself as a victim of cyberwar. Faced with this threat, the countries targeted by I-Soon are calling for strengthening their cooperation and defense in cybersecurity.

For example, the European Union adopted a legal framework in 2023 to impose sanctions on perpetrators of cyberattacks, including China. Likewise, NATO has recognized cyberspace as a domain of operation, and affirmed its willingness to retaliate in the event of an attack. Finally, democratic countries have launched initiatives to promote the values ​​of freedom and transparency on the internet, such as the Partnership for an Open and Secure Cyberspace.

However, these efforts remain insufficient to confront the Chinese threat, which has considerable resources and sophisticated strategies. It is therefore necessary to develop a global and coordinated approach, which involves governments, businesses, organizations and citizens. This would involve strengthening the resilience of information systems, sharing information and good practices, raising users’ awareness of the risks and opportunities of cyberspace, and promoting constructive dialogue with China.

The solutions of Freemindtronic against the cyber espionage threat

Facing the cyber espionage threat, especially from China, requires effective and adapted solutions, both from a technical and a strategic perspective. One of the companies that offers such solutions is Freemindtronic, an Andorran company that develops security and encryption technologies, based on the NFC HSM (Near Field Communication and Hardware Security Module) technology. The NFC HSM technology allows to create hardware security modules on any type of device, that ensure the encryption and the signature of any data, without contact, without energy source, and without internet connection.

Freemindtronic offers several solutions against the cyber espionage DataShielder Defense NFC HSM: a solution for sovereign communications, that allows to encrypt and sign any data on any type of device, with an unmatched level of confidentiality and trust. DataShielder uses the EviCore HSM OpenPGP technology, which is interoperable, retrocompatible, and versatile. DataShielder allows to customize the security of secrets, and to meet various specific needs.

  • PassCypher NFC HSM: a solution for the management and storage of passwords, that allows to create, store, and use complex and secure passwords, without having to remember or enter them. PassCypher uses the EviPass NFC HSM technology, as well as the NFC HSM devices of Freemindtronic, EviTag and EviCard. PassCypher offers a maximum security and a simplicity of use.
  • PassCypher HSM PGP: a solution for the management and storage of PGP keys, that allows to create, store, and use PGP keys, certificates, and signatures, without having to remember or enter them. PassCypher uses the EviCore HSM OpenPGP technology, as well as a hybrid solution via a web extension. PassCypher works without server and without database, and stores the encrypted containers on any storage device, protected by a post-quantum AES-256 encryption.

These solutions of Freemindtronic allow to protect oneself from the cyber espionage threat, by encrypting and signing the data, by managing and storing the passwords and the keys, and by communicating in a confidential and sovereign way. They are based on the NFC HSM technology, which guarantees a hardware and software security, without contact, without energy source, and without internet connection.

The means of counter espionage against the methods of I-Soon

Against the methods of cyber espionage of I-Soon, which are varied and sophisticated, the countries and organizations targeted must implement effective and adapted means of counter espionage. These means can be of several types:

  • Preventive: they consist of strengthening the security of the information systems, by using up-to-date software, antivirus, firewall, complex passwords, encryption protocols, etc. They also consist of training the users to good practices, such as not opening suspicious attachments or links, not disclosing confidential information, not using public or unsecured networks, etc.
  • Defensive: they consist of detecting and blocking the intrusion attempts, by using tools of surveillance, analysis, tracing, filtering, neutralization, etc. They also consist of reacting quickly and limiting the damage, by isolating the compromised systems, backing up the data, alerting the competent authorities, communicating transparently, etc.
  • Offensive: they consist of retaliating and deterring the attackers, by using tools of counter-attack, disinformation, sabotage, sanction, etc. They also consist of cooperating with the allies and partners, by sharing the information, the evidence, the strategies, the resources, etc.

These means of counter espionage must be adapted to the specificities of the methods of I-Soon, which are varied and sophisticated. For example, to face the security flaws, it is necessary to use trustworthy software, verify their integrity, and update them regularly. To face the malware, it is necessary to use efficient antivirus, scan the systems regularly, and clean them in case of infection. To face the social engineering techniques, it is necessary to raise the awareness of the users, verify the identity and the credibility of the interlocutors, and not let oneself be influenced or corrupted.

Chinese cyberespionage statistics

The I-Soon data leak constitutes unprecedented testimony to the scale and impact of Chinese cyberespionage, which is based on close collaboration between the authorities and the private sector. Here are some statistics that illustrate the phenomenon:

China spent at least US$6.6 billion on cyber censorship in 2020, according to the Jamestown Foundation.

According to official sources, at least 2 million people were working for China’s cyberespionage system in 2013, a number that has almost certainly increased over the past eight years.
GreatFire, a censorship monitoring organization in China, estimates that 16% of the world’s 1,000 most visited websites are currently blocked in China.
In 2022, ANSSI handled 19 cyber defense operations and major incidents, compared to 17 in 2021. Nine of them were intrusions attributed to Chinese actors.

In conclusion, the means of counter espionage against the methods of I-Soon are essential to protect the interests and the sovereignty of the countries and organizations targeted. They must be implemented in a coordinated and proportionate way, respecting the principles of legality and legitimacy.

Cyber Resilience Act: a European regulation to strengthen the cybersecurity of digital products

European Commission logo symbolizing the Cyber Resilience Act and NFC HSM technology.

The CRA: Strengthening Cybersecurity Across the EU

Cyber Resilience Act (CRA) is a pivotal European regulation, enhancing cybersecurity standards for digital products. This legislation aims to safeguard users and businesses from cyber threats, ensure market competitiveness, and foster innovation in the cybersecurity field. In this article, we delve into the CRA’s essential features, its advantages and potential challenges, and the implications for manufacturers and distributors of digital products. Discover how the CRA aims to fortify digital security and resilience throughout the European Union.

2025 Cyber Doctrine Cyberculture

Uncodified UK constitution & digital sovereignty

2025 Cyberculture Cybersecurity Digital Security EviLink

CryptPeer messagerie P2P WebRTC : appels directs chiffrés de bout en bout

2025 Cyber Doctrine Cyberculture

Souveraineté individuelle numérique : fondements et tensions globales

2025 Cyberculture

Louvre Security Weaknesses — ANSSI Audit Fallout

Stay informed with our posts dedicated to Cyberculture to track its evolution through our regularly updated topics.

[bws_pdfprint display=’print’]Explore our Cyberculture section for detailed information on the Cyber ​​Resilience Act CRA, authored by Jacques Gascuel, a pioneer in contactless, serverless, databaseless sensitive data security solutions. Stay up to date and secure with our frequent updates.

The Cyber Resilience Act: a European regulation to strengthen the cybersecurity of digital products

The Cyber Resilience Act (CRA) is a European regulation that imposes cybersecurity standards on digital products. It aims to protect users and businesses from cyber threats, harmonise the digital internal market and support innovation in cybersecurity. In this article, we’ll walk you through the key features of the CRA, its pros and cons, and its implications for manufacturers and distributors of digital products.

Introduction au Cyber Resilience Act (CRA)

The EU proposed the Cyber Resilience Act in 2022 to set uniform safety standards for products with digital components, such as internet-connected devices, software and online services. These products can be exposed to cyberattacks that affect their availability, integrity and confidentiality. The CRA aims to protect users and businesses from these risks, by requiring common rules for market entry and cybersecurity measures throughout the product lifecycle. It also establishes a CE marking system to indicate compliance with cybersecurity standards. Moreover, the CRA distinguishes critical products, which have higher obligations according to their level of criticality. The CRA is part of the 2020 EU Cybersecurity Strategy, which seeks to enhance the EU’s collective resilience against cyber threats and foster a secure and trustworthy digital environment for all.

The CRA was approved by the Council and the Parliament in november 2023, and will enter into force in 2024, 20 days after its publication in the Official Journal of the EU. However, it will not be applicable until 2027, to allow a transition period for existing products and software. Moreover, the CRA will be revised every five years, to adapt to technological developments and stakeholder needs.

In this subject, we will explain the main provisions of the CRA, its pros and cons, and its impact on the digital market and society. So,the CRA aims to increase the security and resilience of digital systems in the EU, by imposing strict and binding requirements for the design, development and maintenance of digital products. It also introduces a CE marking system for digital products, ensuring their compliance with established cybersecurity standards.

Strengthening the EU’s Cybersecurity Framework: The Provisional Agreement on the Cyber Resilience Act

A Milestone for a Secure Digital Single Market

The Council presidency and the European Parliament have struck a landmark agreement on the proposed Cyber Resilience Act (CRA), taking a major step forward in fortifying the European Union’s cybersecurity landscape. This critical legislation outlines EU-wide cybersecurity requirements for digital products, addressing the urgent need for a harmonized approach to securing connected devices before they reach consumers.

Hailed as a crucial step by Spanish Minister of Digital Transformation José Luis Escrivá, the agreement emphasizes the essential need for a basic cybersecurity level for all connected devices sold within the EU, ensuring robust protection for both businesses and consumers.

Key Features and Amendments of the Agreement

The provisional agreement preserves the core principles of the European Commission’s proposal, focusing on several key areas:

  • Rebalancing Compliance Responsibility: Manufacturers now take primary responsibility, handling tasks like risk assessments, conformity declarations, and cooperation with authorities.
  • Vulnerability Handling: The agreement mandates processes for manufacturers to ensure ongoing cybersecurity and outlines specific obligations for importers and distributors as well.
  • Transparency and Consumer Protection: Measures are introduced to enhance transparency regarding the security of both hardware and software for consumers and businesses, empowering informed decision-making.
  • Market Surveillance Framework: A robust framework will enforce the regulations, ensuring compliance and safeguarding the EU’s digital space.

Co-legislators have also proposed adjustments, including:

  • Simplified Product Classification: A streamlined approach for classifying regulated digital products, facilitating easier compliance and understanding.
  • Product Lifetime Determination: Manufacturers must specify the expected lifespan of digital products, with a minimum five-year support period, unless shorter use is anticipated.
  • Reporting Obligations: A focus on reporting actively exploited vulnerabilities and incidents, enhancing the role of national authorities and ENISA in managing cybersecurity threats.

Looking Forward: Implementation and Impact

With the provisional agreement in place, technical work continues to finalize the regulation’s details. The compromise text will be presented for endorsement by member states, marking a critical moment in the EU’s journey towards a cohesive and secure digital ecosystem.

The CRA is set to apply three years after enactment, providing manufacturers with ample time to adapt. Additionally, specific support measures for small and micro enterprises have been agreed upon, including awareness-raising, training, and assistance with testing and compliance procedures.

The Path to the Cyber Resilience Act

This provisional agreement marks the culmination of a journey that began with the Council’s 2020 conclusions on the cybersecurity of connected devices, emphasizing the need for comprehensive legislation. Reflecting the urgency expressed by Commission President von der Leyen in 2021 and subsequent Council conclusions, the CRA proposal submitted by the Commission in September 2022 aims to complement the existing EU cybersecurity framework, including the NIS Directive and the EU Cybersecurity Act.

This agreement represents a significant milestone in the EU’s commitment to enhancing cybersecurity resilience, marking a new era of digital product security and consumer protection across the Union.

Business Requirements and Responsibilities

Under the CRA, manufacturers and distributors of digital products are required to ensure the compliance of their offerings from the moment they are placed on the market and throughout their lifecycle. This involves actively monitoring for vulnerabilities and working closely with security researchers to identify and fix potential vulnerabilities within 90 days of discovery.

Cooperation and Sanctions

Another cornerstone of the CRA is the enhanced cooperation between EU Member States and the European Commission to monitor the application of the Regulation. In the event of non-compliance, companies risk severe penalties, up to 10% of their annual global turnover. This underlines the EU’s commitment to ensuring a high level of digital security.

Application and Exclusions of the CRA

The CRA applies to a wide range of digital products, with the notable exception of those already regulated by other EU legislation, such as medical devices or vehicles. Its aim is to close legislative gaps and strengthen coherence in the field of cybersecurity.

Conclusion and Outlook

Following its approval by the Council of the EU and the European Parliament, the CRA is scheduled to enter into force in early 2024. Manufacturers then have 36 months to comply with the new rules. This initiative marks an important step towards a more secure and resilient European Union in the face of digital threats.

Benefits of the Cyber Resilience Act for the Digital Ecosystem

The Cyber Resilience Act (CRA) is envisaged not only as a regulatory framework, but also as a lever for improving cybersecurity at the European Union level. It brings several significant benefits, both for users and for the digital economy as a whole.

Strengthening Consumer and Business Protection

One of the main strengths of the CRA is its ability to raise the level of security for consumers and businesses. By imposing high and constantly updated cybersecurity standards, the regulation ensures that digital products purchased or used offer optimal protection against cyber threats. This helps to create a safer digital environment for all.

Harmonization of the Digital Internal Market

The CRA plays a crucial role in harmonising cybersecurity rules across the EU. By eliminating the fragmentation and divergence of national laws, it facilitates the free movement of digital products within the Single Market. This is essential to support economic integration and boost intra-European trade in digital solutions.

Driving Innovation in Cybersecurity

Finally, the CRA is a driver of innovation in the cybersecurity sector. By increasing demand for secure digital products, it encourages investment in research and development. This dynamic creates valuable opportunities for European companies, allowing them to stand out as leaders in the field of cybersecurity on the global stage.

In sum, the benefits of the CRA are manifested in enhanced protection for users, regulatory harmonisation beneficial to the European single market, and increased support for innovation in the cybersecurity sector. Through these measures, the CRA aims to establish a solid foundation for a safe, competitive and innovative digital ecosystem in the European Union.

Analysis of the Challenges Posed by the Cyber Resilience Act

The Cyber Resilience Act (CRA), while aiming to strengthen digital security within the European Union, raises concerns about its potential impact on various aspects of the digital landscape. These drawbacks deserve special attention to understand the challenges associated with the implementation of this legislation.

Impact on Vulnerability Disclosure

A major criticism is the possible reluctance of security researchers to report discovered vulnerabilities. The fear of sanctions or legal action, due to failure to comply with deadlines or procedures dictated by the CRA, could deter these key players from sharing their findings, thus limiting collective efforts to strengthen cybersecurity.

Effects on Free and Open-Source Software

The CRA is also suspected of slowing down the development and adoption of free and open-source software. The latter, known for their security and transparency, could be subject to disproportionate and onerous compliance requirements. These risks hindering innovation and the use of these valuable resources in the digital ecosystem.

Standardization of Disclosure Models

Another sticking point is the potential reduction in the effectiveness and diversity of vulnerability disclosure models. The one-size-fits-all and rigid approach advocated by the CRA may not be appropriate for all situations, requiring flexibility to adapt to the specifics of each case.

Potentially disproportionate penalties

The penalties envisaged by the CRA for non-compliance are considered by some to be excessive. The prospect of severe financial penalties could jeopardize the economic viability of digital manufacturers and distributors, as well as their ability to innovate. This approach could, therefore, have negative repercussions for the entire digital sector.

In sum, although the CRA aims to establish a strengthened security framework for the European Digital Space, it is crucial to assess and address its possible negative impacts. Careful consideration of these issues will allow the regulation to be adjusted and refined so that it effectively supports cybersecurity without hindering innovation or collaboration in the digital domain.

Cyber Resilience Act Compliance Guide for the Digital Industry

The Cyber Resilience Act (CRA) is a major initiative by the European Union to increase cybersecurity across its Member States. Compliance with this regulation requires a series of targeted and structured actions, applicable to both manufacturers and distributors of digital products.

Actions Required for Digital Product Manufacturers

  • Conducting Cyber Risk Assessments: The first step involves analyzing and documenting the risks associated with the products. This includes identifying threats, vulnerabilities, impacts, and protective measures, with this information regularly updated.
  • Application of the CE Marking and Information to Users: Products must bear the CE marking, a symbol of their compliance with EU safety standards. It is essential to provide comprehensive information on the cybersecurity characteristics of products, including conditions of use and maintenance.
  • Security Updates: Manufacturers must establish and maintain procedures for updating the security of products, ensuring the ability of products to receive and install these updates. Proactive communication about the need for and availability of updates is crucial.
  • Vulnerability Reporting: Discovered or reported vulnerabilities must be reported within 90 days. It is important to communicate corrective actions to users using appropriate channels and adhering to the principles of responsible disclosure.
  • Cooperation with Cybersecurity Authorities: Collaboration with competent authorities, participation in audits and provision of the necessary documents for compliance verification are key elements.

Obligations of Digital Product Distributors

  • Product Conformity Verification: Distributors must ensure that the products marketed comply with the requirements of the CRA, including the CE marking. They must also provide adequate information about the cybersecurity of the products.
  • Security Update Information and Support: Distributors are responsible for notifying users of security updates and assisting them with their installation. Communication about vulnerabilities and remediation is also required.
  • Audit and Cooperation with Authorities: Submission to controls, cooperation with competent authorities and provision of the necessary information to demonstrate compliance are essential.

Importance of Compliance

Failure to comply with CRA guidelines can result in significant penalties, including fines of up to 10% of annual worldwide turnover. The adoption of internal compliance and governance mechanisms is therefore crucial to avoid such consequences.

CRA compliance is not only a legal imperative but also an opportunity to improve the security and resilience of the European digital ecosystem. With these measures, the digital industry makes a significant contribution to data protection and user trust in digital technologies.

Which products are covered by the Cyber Resilience Act?

General definition of the products concerned

The CRA applies to all products with digital elements that are directly or indirectly connected to another device or network, with the exception of those already covered by other EU rules, such as medical devices, aviation or cars. The CRA aims to fill gaps and ensure consistency in existing cybersecurity legislation.

Distinguishing between critical and non-critical products

The CRA applies to a wide range of products with digital components, such as internet-connected devices, software and online services. However, not all products are subject to the same level of scrutiny and obligations. The CRA distinguishes between critical and non-critical products, based on the level of risk they pose to users and society.

The scope of the CRA

The CRA covers all products that have a digital component and that are connected directly or indirectly to another device or network. This includes all connected hardware (computers, phones, household appliances, cars, toys, virtual assistive devices, etc.) as well as systems such as VPNs, antivirus, password managers, software essential to the management of cloud services, or the operating systems of the aforementioned hardware.

For the sake of clarity, the draft CRA provides a list of affected products and software. However, this list is not exhaustive and may be updated by the Commission to take into account technological developments.

The classification of critical products

As you will discover by reading further, this CRA regulation makes a distinction between a general category of products containing digital elements, and those considered “critical”. The latter category represents 10% of the objects covered by this regulation. While critical products are those which, if compromised, would have significant impacts on the security of property and people as well as society.

In summary, this regulation is subdivided into critical products and two other classes according to the level of criticality of the risks. Thus, depending on the class to which they belong, software or hardware will be subject to more or less strict supervision and obligations.

The obligations for different classes of products

To streamline the understanding of the impact of the Cyber ​​Resilience Act (CRA) on product classes, let’s take a look at this simplified guide. This is a table that succinctly classifies products according to their criticality under CRA regulations. As a result, this has the advantage of highlighting the specific obligations as well as their impacts on manufacturers and their potential effects on the market. Therefore, this has the effect of presenting this information in a clear and organized manner. We also aim to facilitate the smooth adaptation process for stakeholders to this Cyber ​​Resilience Act regulation. So prepare now to take this information into account to effectively improve and anticipate your strategies. Anticipate your compliance with its new and evolving European cybersecurity standards.

Table 2: CRA Obligations by Product Class
Product Class Obligations Impact on Manufacturers Market Effects
Most Critical
  • Certification by an independent body before market entry.
  • Incurs significant costs and delays.
  • May hinder innovation and competitiveness, especially in electronics and embedded systems.
Intermediate
  • Self-assessment and declaration of conformity by manufacturers.
  • Reduces administrative burden and time to market.
  • Demands high responsibility and transparency.
Less Critical
  • Compliance with essential requirements, no formal certification needed.
  • Ensures basic security levels without excessive costs.
  • Enhances trust in less critical digital products.

Key Insights:

  • First, the Cyber ​​Resilience Act classifies products based on their impact on cybersecurity and imposes specific compliance obligations on them.
  • This is why the most critical products are subject to strict certification processes.
  • In fact, this affects market dynamics. Whereas, intermediate and less critical classes follow simplified compliance pathways. This balances security needs and market viability.
  • Finally, this concise overview facilitates informed decision making and strategic planning for market positioning and observation.

Navigating the Cyber Resilience Act (CRA): A Quick Guide

We’ve compiled a simplified guide to help you quickly navigate the complexities of the Cyber ​​Resilience Act (CRA). Thus, this table details the objectives of this regulation on the products it covers and the essential requirements it imposes. Additionally, it also highlights the main benefits and potential obstacles of the law. Thus, this brief overview aims to inform you of the essential knowledge to understand and adapt to the implications of the ARC. By familiarizing yourself with these critical aspects now, you can advantageously stay one step ahead. This therefore guarantees you preparation for the expected developments over three years in the cybersecurity landscape within the EU by 2027.

Table 1: Overview of the CRA

Aspect Details
Aim of the CRA
  • To strengthen the cybersecurity of products and software within the EU.
Covered Products and Software
  • Hardware: Smartphones, tablets, smartwatches, desktops, laptops, routers, smart home appliances, POS systems, medical devices, etc.
  • Software: Operating systems (Windows, macOS, Linux), browsers (Chrome, Firefox, Safari), mobile apps, security software, cloud services, etc.
  • Data Storage/Processing: Hard drives, cloud storage, PCs, servers, software handling sensitive data.
Key Requirements
  • Conduct risk assessments
  • Implement security measures
  • Provide information to users
  • Report vulnerabilities
  • Cooperate with authorities
Main Benefits
  • Enhanced user security
  • Increased trust in the digital economy
  • Accelerated innovation in cybersecurity
Potential Challenges
  • Increased costs for compliance
  • Regulatory complexity
  • Risk of market fragmentation
Staying Informed
  • Regular updates and compliance checks are crucial for adherence to the CRA.

Key Takeaways

  • First, the CRA is an essential regulation having an impact on the European cybersecurity framework.
  • Then, this involves compliance with the requirements of the mandatory CRA for manufacturers, distributors and importers.
  • Finally, this has the effect of offering significant advantages but at the same time generates certain additional cost challenges.

In summary, this table format provides a concise and organized summary of the ARC. This makes it easier for you to understand its scope, requirements, benefits and challenges.

Hardware Security Module with the CRA

Under the Cyber ​​Resilience Act (CRA), Hardware Security Modules (HSMs) play a crucial role in securing Europe’s digital infrastructure. Indeed, they are the Guardians of the cryptographic keys. They are in fact the pillars of data security and digital transactions. Without question, HSMs are essential tools to meet the strict requirements of the CRA.

Definition of HSMs

Hardware and digital security modules (HSMs) play a crucial role in securing cryptographic processes. They generate, protect, and manage encryption, decryption, digital signature, and certification keys. Their importance for the protection of sensitive data and digital trust classifies them as critical products according to the Cyber Resilience Act (CRA).

Features of the HSM Hardware

Hardware HSM comes in the form of a physical device, ensuring high security against physical and logical attacks. It can be integrated into a computer system such as a PCI card or an external enclosure. These devices are evaluated and certified according to international safety standards, such as FIPS 140 and Common Criteria EAL4+, attesting to their reliability and robustness.

Benefits of Digital HSM

At the same time, digital HSM offers a software solution that provides security comparable to that of a hardware HSM. With virtualization and advanced encryption, it can be deployed on servers, cloud environments, or mobile devices. Certifications, such as FIPS 140-2 Level 1 or Common Criteria EAL2+, validate the compliance of these software solutions with rigorous security standards.

Cyber-resilience regulation certification process in force

In accordance with the requirements of the CRA, HSMs, whether physical or digital, must obtain certification from an independent body before they are placed on the market. This certification assures users that the devices meet high standards of security and protection of sensitive information.

Importance of HSMs in Cybersecurity

Hardware and digital HSMs are critical components of an organization’s security infrastructure. They secure the exchange of information by providing a reliable and certified method of protection for critical data. By facilitating secure management of cryptographic keys, HSMs build digital trust and support regulatory compliance.

In short, both hardware and digital HSMs are indispensable tools in the modern cybersecurity landscape. Their role in securing cryptographic keys and encryption processes is vital for data protection and trust in digital systems. The mandatory certification emphasizes their importance and ensures that they comply with the highest safety standards.

Hardware Security Modules (HSMs) Under the Cyber Resilience Act

Definition and Features of HSMs

HSMs are specialized devices designed for the secure management of cryptographic keys, crucial for data encryption and transaction security. These modules embody the core principles of the CRA, providing foundational security capabilities across critical and less critical sectors.

Fixed HSMs

Embedded within infrastructural setups, fixed HSMs offer enduring security solutions. These devices are pivotal in safeguarding essential services, from energy distribution to financial transactions, aligning with the CRA’s high-security benchmarks.

Removable HSMs

Offering versatility, removable HSMs, such as USB HSMs, enable secure key management across varied operational contexts. They facilitate a balance between security and mobility, catering to diverse needs within the CRA framework.

NFC HSMs

Merging NFC technology with HSM security, NFC HSMs introduce a new paradigm in contactless transaction security. Although categorized as non-critical, their adherence to CRA standards exemplifies the act’s comprehensive approach to cybersecurity, spanning from retail to access control applications.

NFC HSM and the Cyber Resilience Act (CRA): A Closer Look at Secure Technology

NFC HSM (Near Field Communication Hardware Security Module) represents a technological fusion. It integrates a hardware security module with Near Field Communication (NFC) technology like those manufactured by the Freemindtronic company in Andorra. They also have the particularities of being patented, of operating without a server, without a database and without the user needing to identify themselves or create an account to use them. They are not connected by default. This device provides secure, on-demand wireless interaction between devices over short distances, further protecting the data exchanges they encrypt.

They represent a significant advancement in secure short-range wireless communication by integrating near-field communication (NFC) with the robust security of hardware security modules (HSM). These devices provide enhanced protection of cryptographic keys and sensitive data, facilitating secure, contactless transactions and interactions with ease and flexibility.

Features and Advantages:
  • Enhanced Security: Embedded HSMs safeguard against external threats, ensuring the integrity of cryptographic keys and sensitive data.
  • Secure Authentication: NFC technology supports mutual authentication, minimizing fraud and counterfeiting risks.
  • Ease of Use: Simplified transactions through touch, eliminating manual data entry.
  • Versatility: Can be integrated into a wide array of devices and applications.
Applications:
  • Contactless Payments: Devices equipped with NFC HSM technology facilitate fast and secure transactions, enhancing user convenience and safety.
  • Access Control: These systems manage entry to secure areas, safeguarding physical and digital assets by regulating access to buildings and sensitive data.
  • Tracking and Traceability: NFC HSMs play a crucial role in supply chain management, enabling the authentication and monitoring of goods, ensuring their integrity from origin to destination.
  • Electronic Tickets: Ideal for storing digital tickets for transportation, events, and other services, streamlining the user experience while ensuring security.
  • Contactless Hardware Secrets Manager: A novel application where NFC HSMs manage passwords, encryption keys, secret keys, PIN codes, and 2FA credentials, offering a secure and convenient solution for managing digital identities and access rights across various platforms.

These examples underscore the versatility and security enhancements provided by NFC HSM technology, aligning with the objectives of the Cyber Resilience Act to foster a secure and resilient digital environment across the EU.

Exemplifying CRA Compliance: Freemindtronic’s NFC HSM

Incorporating Freemindtronic’s NFC HSM as a case study offers an insightful lens through which to view the Cyber Resilience Act’s (CRA) implications for digital product security. Freemindtronic’s approach exemplifies adherence to the CRA through its innovative security measures and compliance practices.

Exemplifying CRA Compliance: Freemindtronic’s NFC HSM

As we delve into the CRA’s extensive requirements and scope, practical examples like Freemindtronic’s NFC Hardware Security Modules (HSMs) illuminate how digital products are aligning with heightened security standards.

Meeting CRA’s Fundamental Compliance Demands:

  • Risk Assessment: Freemindtronic has not just conducted a thorough risk evaluation but has also embedded stringent risk management practices from inception through to development, manufacturing, and usage of NFC HSMs. This includes countermeasures against both invasive and non-invasive threats, reflecting the CRA’s directive for integrated risk management.
  • Security Implementations: With patented multi-security functions such as segmented key authentication and customizable trust criteria, alongside post-quantum considered AES-256 encryption in NFC HSM memories, Freemindtronic exceeds the CRA’s requirements for advanced security measures.
  • Vulnerability Disclosure: Freemindtronic’s immediate vulnerability disclosure mechanism, especially through its website, aligns with the CRA’s demand for timely vulnerability reporting to authorities, despite over seven years without detected vulnerabilities in NFC HSM products.
  • Regulatory Cooperation: Freemindtronic’s proactive partnership with Andorran regulatory bodies, including the National Cybersecurity Agency of Andorra (ANC), signifies a commitment to enhancing security collaboratively, as encouraged by the CRA.

Freemindtronic’s NFC HSM Features Enhancing CRA Compliance:

  • Serverless and Database-Free Operation: This minimizes potential attack vectors, aligning with the CRA’s focus on cybersecurity risk reduction.
  • User Anonymity and No Account Creation: By operating anonymously without user identification or account creation, It embodies a contactless plug-and-play principle, making it physically impossible to identify the NFC HSM users. Freemindtronic supports the CRA’s emphasis on user privacy and data protection.
  • End-to-End Anonymization: Freemindtronic’s NFC HSMs are not active by default, given their battery-less design. They are inert products that become active for less than a second during the use of the secret contained within the NFC HSM. Secrets used on the phone or computer are not stored in the systems; everything is conducted ephemerally in volatile memory. This approach is in strict adherence to the CRA’s data protection and confidentiality principles.
  • Innovation Patent Protection: Freemindtronic’s security solutions, underpinned by innovation patents, set a high compliance standard with the Cyber Resilience Act.

Industry Advantages:

  • Simplified Compliance Process: Freemindtronic’s NFC HSMs provide a pre-compliance solution that simplifies adherence to CRA regulations, saving time and resources for businesses.
  • Enhanced Data Security: Freemindtronic sets a security benchmark for sensitive data and cryptographic keys, embodying the CRA’s aim to standardize protection across digital products.
  • Adaptability to Diverse Applications: The flexibility of Freemindtronic’s NFC HSMs showcases the adaptability of security solutions to meet various application needs within the CRA framework.

By showcasing Freemindtronic’s NFC HSMs, we highlight how innovative security technologies can not only meet but surpass the rigorous expectations of the CRA. This insight into Freemindtronic’s compliance strategy offers a practical perspective on adhering to CRA guidelines, reinforcing the regulation’s role in boosting the cybersecurity posture of digital products within the EU.

Key Features of the CRA at a Glance

In summary, the Cyber ​​Resilience Act aims to strengthen the cybersecurity of products sold within the European Union.

This concerns a very large number of products, such as Internet-connected devices, software and online services.

Indeed, manufacturers and distributors will be required to comply with the various requirements of this European CRA regulation. In particular, they will have to carry out risk assessments on their products, implement security measures and inform users.

Thus, the Cyber Resilience Act should offer many advantages. This is characterized by increased user security. But it should also promote trust and the digital economy and help accelerate European innovation in the cybersecurity sector. However, the downside is that the ARC will impose certain challenges, such as increased costs for manufacturers and distributors, increased regulatory complexity and potential fragmentation of the single market.

Overall, the CRA constitutes an important piece of legislation that will have a major impact on the European cybersecurity landscape. It is important that all stakeholders are aware of the ARC requirements and take steps to comply with them.

The table below provides a summary of the CRA’s key features.

Table 1: Summary of the Cyber Resilience Act (CRA)

Feature Benefits Challenges
Scope
  • Wide range of products
  • Exclusion of certain products
Requirements
  • Harmonization of cybersecurity requirements
  • Costs and delays for manufacturers
Compliance
  • Certification process for critical products
  • Market fragmentation
Sanctions
  • Fines for non-compliance
  • Discouragement of vulnerability reporting
Objectives
  • Improved security and resilience
  • Impact on innovation
Impact
  • Protection of users and businesses
  • Difficulty balancing security and innovation

Finally, this table above constitutes a simple summary of the main characteristics of the CRA. So you have a more complete visual understanding of the Cyber ​​Resilience Act.

In conclusion on the European cyber-resilience act regulation

In conclusion, the Cyber Resilience Act (CRA) represents a significant step forward in the European Union’s efforts to strengthen cybersecurity and protect consumers in the digital age. While challenges remain, the CRA has the potential to create a more secure and resilient digital ecosystem for all. As the regulation comes into effect and evolves over time, it will be crucial to monitor its impact and adapt it as needed to ensure its continued effectiveness in a rapidly changing technological landscape. Ultimately, the success of the CRA will depend on the collective efforts of governments, businesses, and individuals to embrace its principles and work together to build a more secure and trustworthy digital world.

Sources

Here are some official sources which confirm this information:

PrintListener: How to Betray Fingerprints

PrintListener technology concept with NFC security solutions.

PrintListener: The Sound of your Fingers can Reveal your Fingerprints

PrintListener emerges as a groundbreaking technology challenging the reliability of fingerprint security. By capturing the unique sound of finger friction on touchscreens, it enables the reproduction of fingerprints. This innovative approach sets PrintListener apart, highlighting its potential to redefine biometric security measures. As we explore its implications, the need for heightened awareness and protective strategies becomes evident.

Stay informed in our posts dedicated to Digital Security to follow its evolution thanks to our regularly updated topics

[bws_pdfprint display=’print’]Learn more through this Digital Security section on the new possibility of corrupting fingerprints written by Jacques Gascuel, creator of data security solutions. Stay informed and safe with our regular updates.

PrintListener: How this Technology can Betray your Fingerprints and How to Protect yourself

PrintListener revolutionizes the realm of Acoustic Analysis Attacks by honing in on the unique sound of finger friction on touchscreens. This novel approach allows for the replication of fingerprints, marking a significant advancement in the field. Unlike traditional techniques that broadly utilize sound to breach security, PrintListener’s methodical focus distinguishes it as a pioneering and distinct attack strategy. This specificity in exploiting fingerprint authentication systems through acoustic signals elevates PrintListener above conventional methods. As we delve deeper into PrintListener, understand the risks it poses to identity and data, and explore protective measures, this article serves as a crucial guide for safeguarding against such innovative threats.

What is PrintListener?

PrintListener is the result of a collaboration between researchers from Zhejiang University, the University of Illinois at Urbana-Champaign, and the University of Washington. They presented their technology at the ACM CCS 2022 conference, one of the most prestigious in the field of computer security. Their paper, titled “PrintListener: Fingerprinting Smartphones from Touchscreen Sound”, describes in detail the working and evaluation of PrintListener¹.

The technology exploits the friction noise of fingers on the screen, which reveals the features of fingerprints. By analyzing this sound with advanced algorithms, PrintListener can create fingerprint copies with high accuracy. You can download the officel document “PrintListener: Uncovering the Vulnerability of Fingerprint Authentication via the Finger Friction Sound“.

How can PrintListener attack fingerprint readers?

Fingerprint readers are increasingly common on smartphones, computers, or applications. They are supposed to offer a high level of security, by verifying the user’s identity from their unique fingerprint.

But PrintListener can fool these readers, by using the fingerprint copies it has generated. The researchers showed that their software could succeed in attacking up to 27.9% of partial fingerprints and 9.3% of full fingerprints in only five attempts, even at the highest security level¹.

Hackers could thus access your accounts, data, or services without your consent. They could capture the sound of your fingers from various sources, such as speakerphone calls, voice messages, or online games.

How to protect yourself against PrintListener?

PrintListener represents a serious threat to biometric security, which was until now considered infallible. To protect yourself against this vulnerability, you should adopt proactive security measures, such as:

  • Updating your antivirus, which could detect and block PrintListener or other malware.
  • Using headphones or earphones, to prevent the sound of your fingers from being captured by the microphone of your smartphone or computer.
  • Activating other authentication modes, such as PIN code or facial recognition, which are less prone to hacking.
  • Changing your passwords regularly, and using strong and different passwords for each account.

How to corrupt a fingerprint?

If PrintListener is not yet available to the public, there are other methods to corrupt a fingerprint. Some are simpler than others, but they all require a certain level of skill and equipment.

  • Making a mold. This involves reproducing the fingerprint of a person from an object they have touched, such as a glass, a door handle, or a keyboard. You then need to use a malleable material, such as clay, wax, or gelatin, to create a faithful imprint. This imprint can then be transferred to a rigid support, such as plastic or metal, to create a fake fingerprint.
  • Using a 3D printer. This involves scanning the fingerprint of a person from a photo, a video, or an optical sensor. You then need to use a 3D modeling software to create a digital model of the fingerprint. This model can then be printed in 3D with a conductive material, such as copper or silver, to create a fake fingerprint.
  • Modifying your own fingerprint. This involves changing the appearance of your fingerprint by using invasive or non-invasive techniques. The invasive techniques consist of injuring, burning, or cutting your finger to modify the lines and ridges of the fingerprint. The non-invasive techniques consist of sticking, painting, or tattooing your finger to mimic the fingerprint of another person.

These methods are more or less effective depending on the type of fingerprint reader used. Some readers are more sensitive than others to the temperature, pressure, conductivity, or depth of the fingerprint. You therefore need to adapt your method according to the reader to attack.

Statistics on fingerprint security

Fingerprint security is widely used in various domains, such as banking, healthcare, law enforcement, or travel. However, it is not flawless, and it can be compromised by different methods, such as PrintListener or others. Here are some statistics on fingerprint security that you should know:

These statistics show that fingerprint security is a popular and growing market, but also a vulnerable and risky one. Therefore, it is important to be aware of the potential threats and to take preventive measures to protect your identity and data.

Summary and further reading

In this article, we have explained what PrintListener is, how it works, how it can attack fingerprint readers, and how to protect yourself against it. We have also provided some statistics on fingerprint security that illustrate the importance and the challenges of this technology.

PrintListener is not the only method to corrupt fingerprint authentication. There are other methods, such as making a mold, using a 3D printer, or modifying your own fingerprint. These methods are more or less effective depending on the type of fingerprint reader used.

If you want to learn more about these other methods, you can read our article (Are fingerprint systems really secure? How to protect your data and identity against BrutePrint), in the Digital Security section of our website. You will find out how they work, what are their advantages and disadvantages, and how to prevent them.

Enhancing Security with EviPass NFC HSM and EviCypher NFC HSM Technologies

Secure Physical Secret Outsourcing

In the wake of vulnerabilities exposed by PrintListener, adopting EviPass NFC HSM and EviCypher NFC HSM technologies becomes crucial. These solutions physically externalize sensitive information like passwords, encryption keys, OTP keys, and enable AES-256 encryption of data and messaging via NFC HSM devices. Even if a device’s fingerprint security is compromised, externally stored secrets remain inviolable, safeguarding encrypted data and messages.

Summary and Conclusion

PrintListener has shed light on significant flaws within fingerprint authentication systems, underscoring the urgent need for enhanced security measures. The integration of EviPass NFC HSM and EviCypher NFC HSM technologies offers a robust solution, physically externalizing and encrypting sensitive information beyond the reach of acoustic fingerprint hacking. This approach not only fortifies biometric security but also ensures the integrity of encrypted data and communications, providing a comprehensive shield against emerging threats.

Encrypted messaging: ECHR says no to states that want to spy on them

ECHR landmark ruling in favor of encrypted messaging, featuring EviCypher NFC HSM technology by Freemindtronic.

Protecting encrypted messaging: the ECHR decision

Encrypted messaging is vital for digital privacy and free speech, but complex to protect. The historic ECHR decision of February 13, 2024 supports strong encryption against government surveillance. We discuss the importance of this decision. You will discover EviCypher NFC HSM encryption technology from Freemindtronic, guardian of this decision but for all messaging services in the world.

2025 Cyber Doctrine Cyberculture

Uncodified UK constitution & digital sovereignty

2025 Cyberculture Cybersecurity Digital Security EviLink

CryptPeer messagerie P2P WebRTC : appels directs chiffrés de bout en bout

2025 Cyber Doctrine Cyberculture

Souveraineté individuelle numérique : fondements et tensions globales

2025 Cyberculture

Louvre Security Weaknesses — ANSSI Audit Fallout

Stay informed in our posts dedicated to Cyberculture to follow its evolution thanks to our regularly updated topics

[bws_pdfprint display=’print’]Learn more through this Cyberculture section on your data encryption rights to protect your personal and professional data written by Jacques Gascuel, creator of data security solutions. Stay informed and secure with our regular news.

Encrypted messaging: ECHR says no to states that want to spy on them

The historic judgment of the European Court of Human Rights (ECHR) elevates encrypted messaging to the rank of guardian of privacy and freedom of expression. But this also poses security and public order problems. On February 13, 2024, she spoke out in favor of strong encryption, against state interference.

The ECHR has rejected Russian authorities’ request to Telegram, a messaging application, to provide private keys for encrypting its users’ communications, or to install backdoors that would allow authorities to access them. The Court considered that this request violated the rights to privacy and correspondence, as well as freedom of expression, of Telegram users.

The context of the case

The case background Six journalists and human rights activists challenged the request of the Russian authorities to Telegram before the ECHR. They claimed that this request violated their fundamental rights. They relied on Articles 8 and 10 of the European Convention on Human Rights. These articles protect the right to privacy and correspondence, and the right to freedom of expression.

The reasoning of the Court

The Court’s reasoning The Court acknowledged that the request of the Russian authorities had a legitimate aim of national security and crime prevention. However, it found that the interference with the rights of the applicants was not proportionate to the aim pursued. It emphasised that encryption plays a vital role in ensuring the confidentiality of communications and the protection of personal data. It held that the request of the Russian authorities was too general and vague. It did not offer enough safeguards against abuse. It could deter people from using encrypted messaging services.

The Court also noted that encryption helps citizens and businesses to defend themselves against the misuse of information technologies, such as hacking, identity theft, data breach, fraud and undue disclosure of confidential information. It stated that this should be duly taken into account when assessing the measures that could weaken encryption.

The Court further observed that, in order to be useful to the authorities, the information must be decrypted at some point. It suggested that the authorities should use other means to obtain the necessary information, such as undercover operations, metadata analysis and international cooperation.

The consequences of the decision

The decision’s implications The decision of the Court is final and binding for Russia. It has to implement it within a reasonable time. It also has a broader impact. It sets out principles applicable to all member states of the Council of Europe, which comprises 47 countries. It sends a strong signal in favour of the respect of fundamental rights on the internet. It aligns with the position of several international organisations, such as the UN, the EU or the OSCE. They have stressed the importance of encryption for the protection of human rights online.

The official link of the ECHR decision is: AFFAIRE PODCHASOV c. RUSSIE and AFFAIRE PODCHASOV c. RUSSIE and AFFAIRE PODCHASOV c. RUSSIE. You can access it by clicking on the title or copying the address in your browser.

The position of other countries in the world

Encryption of communications is not a consensual topic. Countries have different, even opposite, positions on the issue. Here are some examples:

  • The Netherlands have argued for the right to strong encryption. They considered it a human right that must be safeguarded, in the country’s own interest.
  • The United States have repeatedly asked technology companies to provide them with access to encrypted data. They invoked the need to fight terrorism. These requests have been challenged by companies, such as Apple. They refused to create backdoors in their encryption systems.
  • China adopted a cybersecurity law in 2016. It requires companies to cooperate with authorities to provide encryption keys or means to bypass encryption. This law has been denounced by human rights defenders. They fear that it will be used to strengthen the surveillance and censorship of the Chinese regime.
  • The European Union adopted a directive on the protection of personal data in 2016. It recognizes encryption as a technical measure suitable for ensuring the security of data. The EU also supported the development of end-to-end encryption. It funded projects such as the free software Signal, which allows to encrypt calls and messages.

These examples show the divergences and convergences between different countries on the subject of encryption. They also reveal the political, economic and social issues that are at stake.

The world’s reactions to the ECHR decision on Encrypted Messaging

The ECHR decision on Encrypted Messaging has sparked different reactions in the world. Some countries praised the judgment, which boosts the protection of human rights on the internet. Other countries slammed the position of the Court, which undermines, according to them, the judicial cooperation and the national security.

The supporters of the ECHR decision

The Netherlands are among the countries that supported the ECHR decision. They argued for the right to strong encryption, considering it a human right that must be safeguarded, in the country’s own interest. The European Union also backed the Court, reminding that encryption is a technical measure suitable to ensure the security of data, in accordance with the directive on the protection of personal data adopted in 2016. The EU also stressed that it funds the development of end-to-end encryption, through projects such as the free software Signal, which allows to encrypt calls and messages.

The opponents of the ECHR decision

The United States are among the countries that opposed the ECHR decision. They have repeatedly asked technology companies to provide them with access to encrypted data, invoking the need to fight terrorism. These requests have been challenged by companies, such as Apple, which have refused to create backdoors in their encryption systems. China also expressed its disagreement with the Court, stating that encryption of communications fosters the dissemination of illegal or dangerous content, such as terrorist propaganda, child pornography or hate speech. China recalled that it has adopted in 2016 a cybersecurity law, which requires companies to cooperate with authorities to provide encryption keys or means to bypass encryption.

The non-signatories of the European

Convention on Human Rights Some countries have not reacted to the ECHR decision, because they are not signatories of the European Convention on Human Rights. This is the case for example of Russia, which ceased to be a member of the Council of Europe on March 16, 2022, after the invasion of Ukraine decided by the Kremlin. The country no longer participates in the activities of the ECHR. This is also the case of many countries in Africa, Asia or Latin America, which are not part of the Council of Europe and which have not ratified the Convention.

The signatory countries of the European Convention on Human Rights

The European Convention on Human Rights is an international treaty adopted by the Council of Europe in 1950, which aims to protect human rights and fundamental freedoms in the states parties. It entered into force in 1953, after being ratified by ten countries: Belgium, Denmark, France, Ireland, Italy, Luxembourg, the Netherlands, Norway, Sweden and the United Kingdom .

Since then, the Convention has been ratified by 36 other countries, bringing the total number of states parties to 46. They are: Albania, Germany, Andorra, Armenia, Austria, Azerbaijan, Bosnia and Herzegovina, Bulgaria, Cyprus, Croatia, Estonia, Finland, Georgia, Greece, Hungary, Iceland, Latvia, Liechtenstein, Lithuania, Malta, Moldova, Monaco, Montenegro, North Macedonia, Poland, Portugal, Romania, Russia, San Marino, Serbia, Slovakia, Slovenia, Spain, Czech Republic, Turkey and Ukraine.

All these countries recognize the jurisdiction of the European Court of Human Rights (ECHR), which is in charge of ensuring the respect of the Convention. The ECHR can be seized by any person, group of persons or non-governmental organization who claims to be a victim of a violation of the Convention by one of the states parties. The ECHR can also be seized by a state party who alleges that another state party has violated the Convention. The ECHR delivers judgments that are final and binding for the states parties.

An innovative and sovereign alternative: the EviCypher NFC HSM technology

Facing the challenges of encryption of communications, some users may look for an alternative more innovative and sovereign than the traditional messaging applications. This is the case of the EviCypher NFC HSM technology, developed by the Andorran company Freemindtronic. This technology makes it possible to generate, store, manage and use AES-256 encryption keys to encrypt all communication systems, such as WhatsApp, sms, mms, rcs, Telegram, webmail, email client, private messaging like Linkedin, Skype, X and even via postal mail with encrypted QR code messages, etc.

EviCypher NFC HSM: A Secure and Innovative Solution for Encrypted Messaging

Firstly, it guarantees the confidentiality and integrity of data, even if the messaging services are compromised for any reason, including by a court order. Indeed, it is physically impossible for Freemindtronic, the manufacturer of the DataShielder products, to provide encryption keys generated randomly by the user. These keys are stored encrypted in AES-256 via segmented keys in the HSM and NFC HSM. Only the user holds the decryption keys, which he can erase at any time.

Secondly, it preserves the anonymity and sovereignty of users, because it works without server and without database. It does not require internet connection, nor user account, nor phone number, nor email address. It leaves no trace of its use, nor of its user. It does not depend on the policies or regulations of the countries or companies that provide the communication services.

Thirdly, it offers an extreme portability and availability of encryption keys, thanks to the NFC technology. The user can carry his encryption keys on a physical support, such as a card, a bracelet, a key ring, etc. He can use them with any device compatible with NFC, such as a smartphone, a tablet, a computer, etc. He can also share them with other trusted users, in a simple and secure way.

Lastly, it is compatible with the EviCore NFC HSM or EviCore HSM technology, which allows to secure the access to equipment and applications. The user can thus use the same physical support to encrypt his communications and to authenticate on his different digital services.

The EviCypher NFC HSM technology guarantees the confidentiality and integrity of data, even if the messaging services are compromised for any reason, including by a court order. Indeed, it is physically impossible for Freemindtronic, the manufacturer of the DataShielder products, to provide encryption keys generated randomly by the user. These keys are stored encrypted in AES-256 via segmented keys in the HSM and NFC HSM. Only the user holds the decryption keys, which he can erase at any time.

Transforming Encrypted Messaging with EviCypher NFC HSM

The European Court of Human Rights (ECHR) decisively highlights encrypted messaging’s vital role in protecting privacy and freedom of speech. EviCypher NFC HSM, aligning perfectly with these principles, emerges as a pioneering solution. It confronts the challenges of state surveillance and privacy breaches head-on, providing unmatched defense for private communications. EviCypher NFC HSM goes beyond the ECHR’s conventional security and privacy requirements. It crafts an inviolable communication platform that honors users’ privacy rights profoundly. With its innovative approach, EviCypher NFC HSM introduces new data protection standards, forging a robust barrier against government intrusion.

Global Reach and User Empowerment

EviCypher NFC HSM’s technology has a broad global impact, seamlessly addressing the varied encryption landscapes worldwide. It provides a consistent answer to privacy and security issues, disregarding geographic limits. This global applicability makes EviCypher NFC HSM an indispensable tool for users worldwide, solidifying its position as a guardian of global privacy.

Despite potential skepticism about new technologies, the user-friendly and accessible nature of EviCypher NFC HSM aims to dispel such doubts. It promotes wider adoption among those seeking to enhance their communication security. Its compatibility with diverse devices and straightforward operation simplify encryption, facilitating an effortless shift towards secure communication practices.

EviCypher NFC HSM: A Beacon of User Autonomy

EviCypher NFC HSM technology deeply commits to empowering users. It allows individuals to generate, store, and manage their encryption keys independently, giving them direct control. This autonomy not only improves data security but also demonstrates a strong commitment to protecting users’ fundamental rights. It resonates with the values emphasized across the discussion, providing an effective way to strengthen online privacy and security. EviCypher NFC HSM marks a significant leap forward in the movement towards a more secure and private digital landscape.

This technologie HSM stands out as a state-of-the-art, self-sufficient solution, perfectly in line with the ECHR’s decisions and the worldwide need for secure encrypted communication. It leads the charge in advancing user autonomy and security, signaling a crucial evolution in encrypted messaging towards unparalleled integrity.

Incorporating EviCypher’s distinctive features—its operation without servers or databases, interoperability, and backward compatibility with all current communication systems, such as email, SMS, MMS, RCS, and social media messaging, even extending to physical mail via encrypted QR codes—highlights its adaptability and innovative spirit. EviCypher’s resistance to zero-day vulnerabilities, due to encrypting communications upfront, further underscores its exceptional security. Operating anonymously and offline, it provides instant usability without requiring user identification or account creation, ensuring seamless compatibility across phone, computer, and communication systems.

Summary at encrypted messaging

Encrypted Messaging is crucial for the digital society. It protects internet users’ privacy and freedom of expression. But it also challenges security and public order. The European Court of Human Rights (ECHR) supported strong encryption on February 13, 2024. It defended the right to encryption, against states that want to access it. Several international organizations agree with this position. They emphasize the importance of encryption for human rights online. However, the ECHR decision sparked diverse reactions worldwide. Different countries have different views on encryption.

Our conclusion on Encrypted Messaging

EviCypher NFC HSM technology is an innovative and sovereign alternative for Encrypted Messaging. Users can generate, store, manage and use AES-256 encryption keys. They can encrypt all communication systems, such as WhatsApp, sms, mms, rcs, Telegram, webmail, email client, etc. EviCypher NFC HSM technology ensures data confidentiality and integrity. It works even if messaging services are compromised. It preserves users’ anonymity and sovereignty. It does not need server or database. It offers extreme portability and availability of encryption keys, thanks to NFC technology. It is compatible with EviCore NFC HSM or EviCore HSM technology. They secure access to equipment and applications.

DataShielder products provide EviCypher NFC HSM technology. They are contactless encryption devices, guardians of keys and secrets. Freemindtronic, an Andorran company specialized in NFC security, designs and manufactures them.

BitLocker Security: Safeguarding Against Cyberattacks

A visual representation of BitLocker Security featuring a central lock icon surrounded by elements representing Microsoft, TPM, and Windows security settings.

BitLocker Security — Windows encryption, recovery mode, TPM 2.0, physical attacks and cryptographic sovereignty — November 2026.

© 2026 Jacques Gascuel — Freemindtronic®. All rights reserved. Original editorial analysis and scientific positioning. Third-party research and vulnerability disclosures remain attributed to their respective authors.

BitLocker Security: Historical Reference, Vulnerabilities, TPM Attacks and Encryption (2006–2026)

[bws_pdfprint display=’print’]

BitLocker Security — express summary

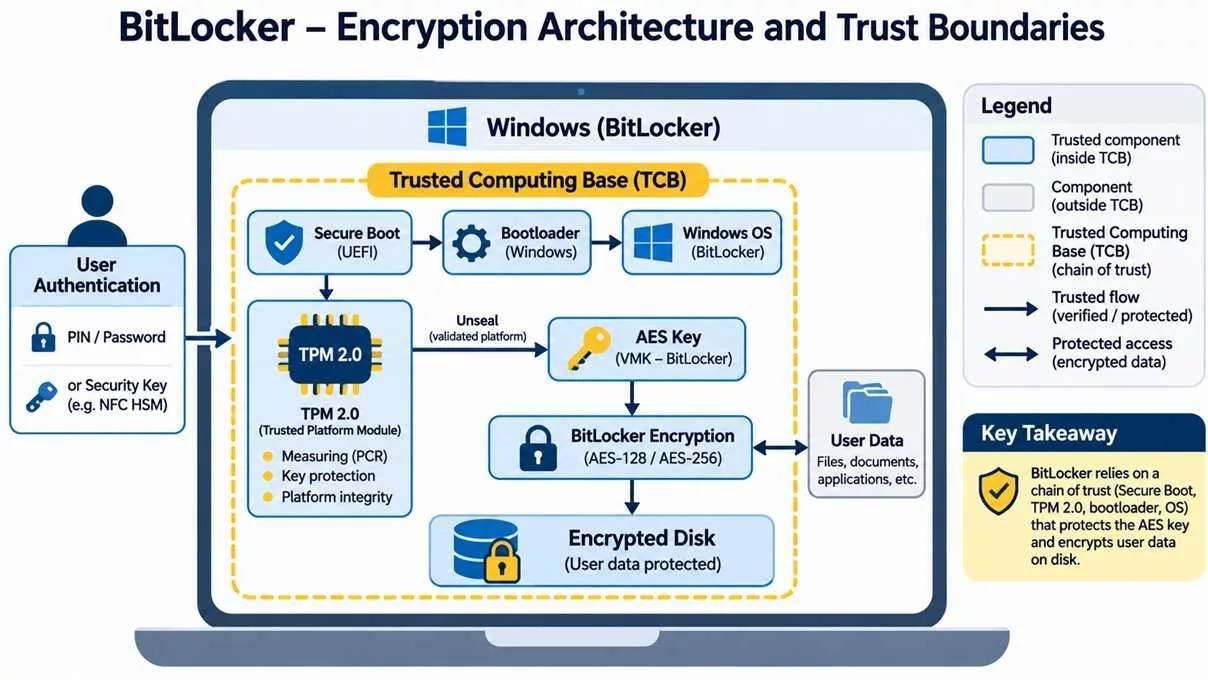
At the volume level, BitLocker protects Windows data using AES encryption. Its effectiveness, however, depends on the complete chain of trust governing access to cryptographic keys, from the TPM and boot environment to recovery procedures and system memory.

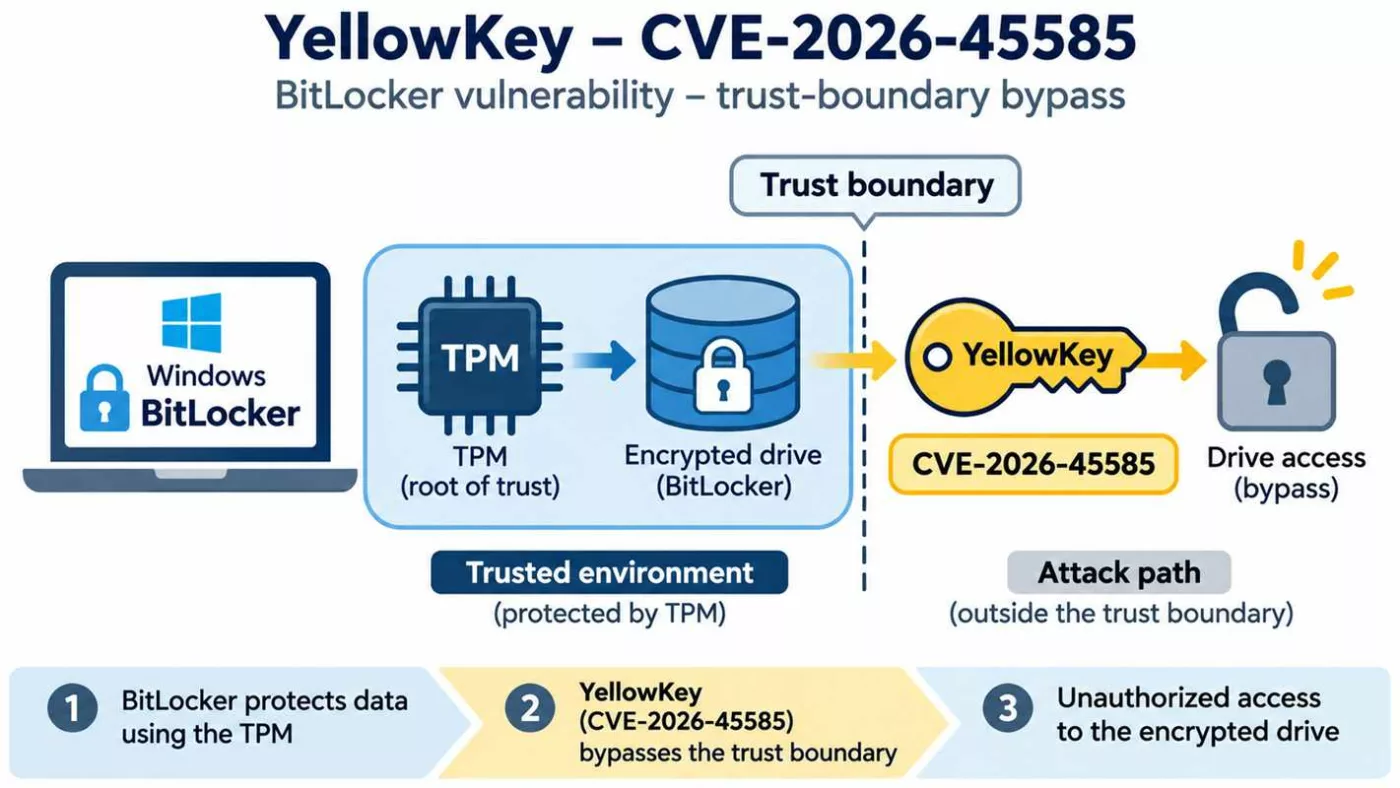
On November 10, 2026, Microsoft disclosed two additional physical security bypass vulnerabilities: CVE-2026-97015 (CVSS 6.8) and CVE-2026-119832 (CVSS 5.9). These disclosures follow the public YellowKey vulnerability (CVE-2026-45585) in May 2026.

None of these disclosures establishes a mathematical break of AES. This guide explains the distinction between encryption strength and operational security, how to recover access after Windows updates, and how independent encryption and external secret management can complement BitLocker.

Immediate action: install applicable security updates, verify protection status and recovery credentials, and assess pre-boot authentication according to your physical threat model.

Reading parameters

Initial publication: February 10, 2024
Last updated: November 16, 2026
Language: EN
Complexity: Intermediate / expert
Editorial type: Living historical, scientific and technical cybersecurity reference
Main topic: BitLocker security
Secondary topics: TPM 2.0, WinRE, Secure Boot, recovery keys, physical attacks, AES and independent encryption.
Author: Jacques Gascuel, inventor and founder of Freemindtronic®.

Publication status

Documentary security analysis, not an independent laboratory qualification or product certification. Vulnerability ratings are attributed to their published records. No unpublished exploit or proprietary implementation is disclosed.

Editorial transparency — FM-AI-2025-11-SMD5 V1.1. This article distinguishes vendor disclosures, published scientific research, architectural analysis and editorial recommendations. AI-assisted technical illustrations are conceptual representations subject to human verification and validation. Their intellectual property rights, attribution and conditions of use are governed by the applicable provisions of the Freemindtronic AI Transparency Declaration.

Executive summary

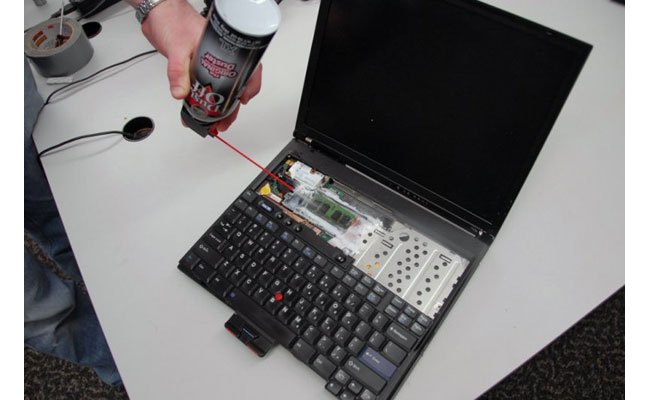
Full-volume encryption reduces exposure when a device is lost, stolen or powered off. It does not guarantee confidentiality after the volume has been unlocked. The November 2026 disclosures reinforce the importance of evaluating authorisation, recovery, hardware trust and memory exposure separately.

Key points

  • Physical access is a prerequisite for the two newly disclosed November CVEs.
  • TPM + PIN reduces selected pre-boot risks but is not universal protection.
  • Recovery credentials must be protected independently.
  • Separately encrypted files may remain protected after a volume encryption bypass.

1. Latest BitLocker vulnerabilities — November 2026

The following selected disclosures are attributed to Microsoft. The scores are CVSS 3.1 base scores, not a universal assessment of organisational risk.

CVE Published CVSS 3.1 Weakness Access Privileges
CVE-2026-97015 10 Nov 2026 6.8 / Medium Heap memory overflow (CWE-122) Physical None
CVE-2026-119832 10 Nov 2026 5.9 / Medium Improper permissions Physical Low
CVE-2026-45585 (YellowKey) 19 May 2026 See advisory Security bypass Physical See advisory

Both November records describe low-complexity physical attacks without user interaction. CISA assessments dated November 10–11 recorded no known exploitation at that time; this is not proof that exploitation has never occurred.

Historical disclosures from 2022 and 2024

The original reference discussed CVE-2022-41099 and CVE-2024-38058. The historical text dated the disclosures to November 2022 and January 2024 and described manual administrative mitigation. Its associations with KB5012170 and KB5024487, respectively, and its historical release-date claims remain unverified. Consult MSRC for the actual affected products and applicable fixes; these legacy associations are not patch instructions.

Selected Windows version thresholds

Windows version CVE-2026-97015 CVE-2026-119832
11 26H2 26300.9711 26300.9974
11 26H1 28000.3231 28000.3501
11 25H2 26200.9711 26200.9974
11 24H2 26100.9711 26100.9974
11 23H2 22631.7652 22631.7711
10 22H2 19045.7807 19045.7846
10 21H2 19044.7807 19044.7846

Selected fixed-version thresholds from the vulnerability records, not a complete product or KB list. Verify applicable updates and servicing eligibility with Microsoft.

2. YellowKey — CVE-2026-45585

YellowKey CVE-2026-45585 vulnerability diagram showing a Windows BitLocker TPM protection trust-boundary bypass and unauthorized encrypted drive access.
YellowKey CVE-2026-45585: conceptual illustration of a BitLocker trust-boundary bypass enabling unauthorised access to encrypted data without breaking the AES encryption algorithm.

Microsoft published the YellowKey record on May 19, 2026 after a public proof of concept became available. The case concerns a security bypass associated with Windows recovery mechanisms. It illustrates why trusted recovery paths must be included in an encryption threat model.

Consult the current vendor advisory for updates and mitigation details. Microsoft identifies TPM + PIN as a mitigation for the documented scenario; claims of alternative variants should not be treated as established without reproducible evidence. A vulnerability alone does not establish intentional backdoor design.

Official CVE record · Microsoft advisory

Practical hardware-based mitigation: PassCypher NFC HSM, capable of generating secrets of up to 512 bits, can facilitate TPM + PIN adoption through independent hardware-based credential storage and automated input using EviKeyboard with InputStick or proprietary end-to-end encrypted EviBLE HID technology. See sovereign pre-boot authentication and YellowKey mitigation.

Historical context: The reference first published on 10 February 2024 is integrated into the thematic chapters below. Its 2025 recovery-guide revision is retained through the historical incident and configuration guidance. BitLocker also protects removable media and virtual drives; secure disposal depends on effective encryption and key custody.

3. BitLocker encryption architecture and trust boundaries

BitLocker encryption architecture diagram showing TPM 2.0, Secure Boot, Windows bootloader, AES-256 disk encryption and trusted computing boundaries.
BitLocker encryption architecture and trust boundaries: TPM 2.0, UEFI Secure Boot, Windows authentication, cryptographic key protection and AES-128/256 disk encryption. The diagram is conceptual; the VMK protects the FVEK, and external NFC HSMs are not native BitLocker protectors.

Architecturally, BitLocker encrypts volumes using AES, including XTS-AES configurations. The Full Volume Encryption Key (FVEK) encrypts volume data; the Volume Master Key (VMK) protects the FVEK. Key protectors govern access to the VMK. A TPM can bind key release to platform measurements and additional authentication conditions.

TPM 2.0 is not a general-purpose RAM protection mechanism. After unlocking, cryptographic material may be available in host memory. Secure Boot authenticates boot components; measured boot records measurements. These functions are complementary, not interchangeable.

Platform measurements + configured authentication
                 ↓
       Key protector authorisation
                 ↓
         Volume Master Key (VMK)
                 ↓
      Full Volume Encryption Key (FVEK)
                 ↓
          Encrypted volume data

This simplified diagram represents the normal unlocking path, not every recovery or protector configuration.

4. Physical attacks, TPM and forensic risks

TPM 1.2 and TPM 2.0 also support cryptographic identity and signature operations. Biometric authentication may use TPM-backed credentials, but this does not mean that biometric templates or all disk keys reside inside the TPM.

TPM 1.2 and TPM 2.0 provide protected key operations, random number generation and signatures. The latter extends algorithm support and authorisation capabilities; neither directly controls host RAM. Platform compatibility and implementation quality remain important.

4.1 Cold boot and memory remanence

Physical controls include locks, safes and secure storage. Hardware and software acquisition tools may be costly or difficult to obtain, although some attacks use inexpensive equipment. These practical constraints are not guarantees of confidentiality.

Residual RAM contents can expose active encryption material on susceptible devices. TPM anti-dictionary protections do not prevent extraction of keys already present in memory. Prefer complete shutdown before loss of physical control and evaluate platform-specific memory protections.

Cold boot attack illustration
Historical illustration: memory remanence and physical access.


Cold Boot research demonstrated that residual DRAM contents decay over time and that cooling can prolong retention on susceptible hardware. Live RAM analysis is a related but distinct forensic technique. Capacity to recover usable keys depends on memory state, equipment and platform protections. Firmware-supported Memory Overwrite Request (MOR) can reduce exposure; neither a startup PIN nor TPM lockout invalidates keys already recovered.

Scientific reference: Halderman et al. (2008).


4.2 DMA attacks

DMA-capable peripherals can threaten host memory on vulnerable systems. Enable Kernel DMA Protection where supported and restrict untrusted peripherals.

Thunderclap DMA attack diagram
Historical illustration: Thunderclap and DMA attack surfaces.

Thunderclap (2019) examined IOMMU isolation across Windows, Linux and macOS. FireWire, Thunderbolt and external PCIe require appropriate port and DMA policies; PCILeech is a historical example of a memory acquisition tool. Encrypting external storage protects its contents, not the host against malicious DMA. See Thunderclap research.

4.3 TPM communication and faulTPM

Published research has demonstrated interception of discrete TPM communications on selected systems and attacks against specific firmware TPM implementations. These findings do not imply that every TPM is vulnerable. The Raspberry Pi Pico demonstration discussed in the original article illustrates the importance of hardware-specific qualification.

Discrete TPM buses, SRTM and firmware TPMs

TPM-only mode allows normal unattended unlocking. Historically, discrete TPM bus interception using inexpensive hardware has illustrated why physical access matters. Stacksmashing’s Raspberry Pi Pico demonstration used a susceptible laptop and Dislocker; it is distinct from the Bus Pirate, a multiprotocol electronic interface supporting SPI, I2C, UART, 1-wire, 2-wire, 3-wire and HD44780 LCD interfaces. Results must not be generalised to every TPM or bus.

Separately, SRTM power-state and measurement attacks and AMD faulTPM research challenge different trust assumptions. Historical references to Intel and Dell platforms require model-specific evidence. Physical isolation, tamper-evident seals, protected bus design (including hardware-specific SPI access controls or firewalls where available), firmware updates and appropriate pre-boot authentication reduce selected risks. Intel CSME and remote attestation may contribute to platform integrity assessment, but are not universal countermeasures.

4.4 TPM implementation defects

CVE-2023-1017 and CVE-2023-1018 concern memory-boundary defects in TPM implementations, not inherently physical fault injection. Consult the hardware vendor for affected firmware and fixes.

Historical reports also identified affected Lenovo systems with Nuvoton TPM implementations. Verify the actual firmware and vendor advisory rather than assuming that all devices share the defects or that BitLocker keys can always be extracted.

4.5 Hardware debugging and fault injection

Hardware debug interfaces such as Intel DCI and fault injection can create additional attack surfaces under specific platform conditions. Disable unauthorised debugging and assess firmware protections. No universal BitLocker decryption capability is established by these attack categories.


Fault injection explores voltage, temperature, radiation and electrical glitching effects on hardware. In contrast, Intel DCI debugging can expose live memory on suitably configured platforms, potentially including the VMK. On a suitably exposed platform, CPU halt and debug-based memory acquisition may enable forensic decryption without the Windows login password or recovery password; this remains configuration-dependent. These are distinct from TPM command-parser defects. Fault-resistant hardware and restricted debug access are relevant controls; remote attestation can report selected measurements but cannot establish immunity.

5. How to fix BitLocker Recovery Mode after a Windows update

Windows updates, firmware changes and changes to measured boot state can trigger recovery. The July 2024 update incident remains a useful historical example. Do not assume a particular PCR change is the cause on every device.

Historical case: July 2024 recovery incident

KB5040442 was associated in the historical article with unexpected recovery prompts. The original explanation attributed this to PCR4, but that causal attribution is unverified. Firmware, bootloader and hardware changes can alter measured state. Review release notes, prepare recovery backups and avoid removing PCR measurements simply to suppress prompts. The incident illustrates the importance of update preparation and vendor communication.

Recovery procedure

  1. Record the recovery key identifier shown on screen.
  2. Retrieve the matching 48-digit recovery password from your authorised backup or organisation.
  3. Enter it on the trusted recovery screen.
  4. After booting, verify Windows update status and BitLocker protection.
  5. If recovery repeats, consult the device vendor or IT administrator before changing firmware, TPM or PCR settings.

Do not clear the TPM, remove protectors or weaken PCR policy merely to suppress recovery prompts. If you cannot recover the credentials, there is no supported universal method to decrypt an intact protected volume.

Microsoft account recovery keys (if backed up to that account).

6. Secure configuration and verification

Consider hardware and software compatibility before deployment. In addition, choose used-space-only or full-volume encryption according to whether previously stored data may remain in unused sectors. For existing devices, assess residual data before selecting the faster option.

Use a supported Windows edition and servicing channel. Full BitLocker management is available on supported Pro, Enterprise and Education editions; qualifying Home devices may offer Device Encryption. Select encryption and protector policies before deployment, preserve recovery credentials and use TPM + PIN where physical risks justify it.


Activation and encryption choices

Check TPM status in Windows Security or TPM management. If required, consult the manufacturer before enabling TPM in UEFI (entry keys can include F2, F12, Del or Esc) or updating firmware. Choose supported protectors for the volume type: TPM + PIN, startup key, password or recovery protector as applicable. Certificate-based protectors have specialised removable-drive uses.

Choose AES-CBC or XTS-AES according to compatibility requirements; XTS-AES is preferred for modern fixed volumes. Evaluate AES-128 versus AES-256, hardware acceleration and performance. Open Manage BitLocker in Control Panel, select the volume, back up recovery credentials and follow the activation wizard. Encryption duration varies with volume size and data.

Verification commands

Run these read-only commands from an elevated PowerShell session:

Get-BitLockerVolume
Get-Tpm
Confirm-SecureBootUEFI
reagentc /info
winver

Verify that protection is on, identify protector types, check the installed Windows version and confirm WinRE status. Avoid publishing recovery passwords or identifying key material in diagnostic logs.

7. Freemindtronic — independent cryptographic protection

Externalizing credential storage and separately encrypting sensitive data introduces additional trust boundaries. EviPass NFC HSM and PassCypher can complement credential management. EviCypher NFC HSM and DataShielder provide a separate encryption approach. EviKeyboard BLE provides a complementary credential input mechanism.

These technologies are not patches for BitLocker CVEs. External storage of secrets does not itself guarantee that credentials entered into a compromised host remain confidential. Independently encrypted files can remain protected after BitLocker is bypassed if their keys and plaintext are not accessible to the attacker.


PassCypher NFC HSM, EviPass, EviKeyboard and EviBLE

The original account describes password-free contactless credential management and smartphone-assisted remote input into BIOS or disk-startup fields, where supported by the host. The historical USB HID analysis distinguishes the USB controller, chipset, processor and TPM; input buffers along this path may expose secrets. Product-specific transport and pairing properties require verification for the deployed version.

Contactless credential storage and smartphone-assisted input can reduce reliance on locally stored secrets. EviKeyboard BLE can deliver supported pre-boot credentials through USB HID where firmware accepts the keyboard. The historical article describes AES-128 CBC for its BLE transport; this product-specific claim requires version-specific verification. Host USB buffers, chipset and input processing may still expose credentials in memory. Physical acquisition requires suitable access and equipment, while memory volatility can limit recovery.

PassCypher’s historical features include sandboxed URL checks, anti-typosquatting, password integrity checks and Browser-in-the-Browser (BTIB) phishing protections. These reduce selected risks but cannot eliminate deception. High-entropy generated passwords must comply with the actual protector’s length and character restrictions; a generated secret exceeding 256 bits does not make a BitLocker PIN a 256-bit key.

High-entropy secret generation: up to 512 bits

PassCypher NFC HSM can generate cryptographic secrets of up to 512 bits, exceeding the nominal key length of AES-256. A uniformly random 512-bit secret has a theoretical search space of 2512 possibilities, compared with 2256 for a 256-bit key.

This generation capacity enables users to create highly unpredictable authentication secrets without relying on human memory or predictable password construction.

However, BitLocker imposes its own authentication format, length and character restrictions. PassCypher can generate secrets adapted to these constraints, including complex enhanced startup PINs. The effective entropy depends on the accepted character set, secret length and generation method.

This capability does not transform AES-256 into AES-512 or provide BitLocker with 512-bit encryption strength.

External hardware-based BitLocker credential management

PassCypher NFC HSM enables independent hardware-based custody of BitLocker startup PINs and recovery passwords. Consequently, users can manage these sensitive credentials outside the computer they protect, without requiring memorisation of complex authentication secrets.

Freemindtronic provides two complementary credential delivery approaches:

  • EviKeyboard with InputStick: smartphone-assisted credential input through an external USB HID keyboard emulator, including supported BIOS, UEFI and BitLocker pre-boot environments.
  • EviBLE HID: Freemindtronic’s proprietary end-to-end encrypted Bluetooth Low Energy secure keyboard emulation technology for credential delivery through compatible endpoints.

These approaches must be distinguished from native operating system Bluetooth keyboard pairing. Pre-boot operation requires a compatible receiving interface recognised by the target firmware and BitLocker environment.

The 48-digit BitLocker recovery password can also be managed independently within the NFC HSM. Its native format and cryptographic properties remain defined by Microsoft.

Mitigating YellowKey through sovereign pre-boot authentication

Microsoft identifies TPM + PIN as a mitigation against the documented YellowKey vulnerability (CVE-2026-45585).

By combining external hardware-based secret management with automated credential input, PassCypher NFC HSM, EviKeyboard and EviBLE can facilitate the adoption of stronger pre-boot authentication without the inconvenience of memorising complex PINs.

Cryptographic sovereignty and defence in depth. Rather than replacing BitLocker or its trusted platform module, Freemindtronic’s technologies introduce an independent hardware-based credential custody boundary. This approach supports stronger authentication configurations while maintaining user control over externally managed secrets.

The mitigation against YellowKey derives from the TPM + PIN configuration documented by Microsoft, rather than from an increase in AES key length.

The effectiveness of this architecture against CVE-2026-97015 and CVE-2026-119832 remains subject to specific technical qualification. External credential custody and encrypted transmission do not prevent every attack against a compromised host or recovery environment. Applicable Microsoft security updates remain essential.

DataShielder and EviCypher

The historical design describes AES-256 independent data encryption, randomly generated and segmented keys, external HSM/NFC HSM custody and transient operational key destruction, including HSM PGP contexts. These mechanisms can reduce exposure to TPM bus interception and fault injection when the independent trust boundary remains intact. Key erasure effectiveness and plaintext exposure require implementation-specific assessment; no near-zero recovery probability is established here.

Post-quantum algorithms do not inherently resolve memory corruption, access control defects or insecure key release.

Historical timeline of BitLocker security (2006–2026)

BitLocker emerged with Windows Vista in 2006–2007. Since then, its threat model has evolved from disk theft towards hardware, firmware, recovery and identity attacks. The following selected milestones distinguish product evolution from security research.

Period Milestone Security significance
2006–2007 Windows Vista Initial BitLocker deployment.
2008 Halderman et al. — Lest We Remember: Cold Boot Attacks on Encryption Keys (2008) Memory remanence challenges data-at-rest assumptions.
2009 Windows 7 / BitLocker To Go Removable storage protection.
2012–2013 Windows 8 / 8.1 UEFI Secure Boot and wider device encryption.
2015 Windows 10 version 1511 XTS-AES support.
2018–2019 Meijer and van Gastel — Self-encrypting deception, IEEE S&P 2019 SSD firmware becomes a critical trust dependency.
2021 Windows 11 TPM 2.0 baseline on supported hardware.
2022–2023 BlackLotus and TPM research Boot trust and hardware implementation risks.
2024 Freemindtronic reference; July recovery incident; BitPixie research Operational recovery and downgrade exposure.
2025 BitUnlocker Recovery-path trust defects.
2026 YellowKey; academic survey; Secure Boot CA transition; November CVEs Continuing evolution of attack surfaces.

Further reading: Microsoft — BitLocker overview and Kenchaiah et al. — The Hardware Isolation Gap, Electronics 15(9), 1959 (6 May 2026). This is a selected chronology, not an exhaustive CVE register.

BitUnlocker (2025): Windows Recovery Environment vulnerabilities

Microsoft researchers Netanel Ben Simon and Alon Leviev presented BitUnlocker at Black Hat USA 2025 and DEF CON 33. Their findings concern the conditions under which recovery software can access a protected volume. Consequently, a trusted recovery environment must be evaluated as part of the security boundary.

CVE Affected trust decision
CVE-2025-48800 Authorisation of scheduled recovery operations
CVE-2025-48003 Trust verification of recovery applications
CVE-2025-48804 Integrity verification of recovery boot images
CVE-2025-48818 Boot configuration and recovery decryption authorisation

Mitigation and relevance to YellowKey

All four discoveries received fixes in July 2025. Moreover, Microsoft recommends TPM + PIN and secure boot-component version enforcement (REVISE). YellowKey is a later disclosure involving recovery trust; however, common attack surfaces do not establish a shared root cause. Source: Microsoft STORM — BitUnlocker (13 August 2025).

BlackLotus, BitPixie and BitLocker downgrade attacks

Administrative UEFI passwords and restriction of legacy boot options can complement revocation policy. However, they do not replace supported security updates or validated recovery media.

BlackLotus and UEFI bootkits

BlackLotus illustrates how a vulnerable signed boot component can undermine Secure Boot. CVE-2022-21894 concerns a Secure Boot bypass, whereas CVE-2023-24932 underlies subsequent revocation guidance. Neither is a mathematical attack against AES. See Microsoft — BlackLotus investigation guidance (2023).

BitPixie and REVISE

BitPixie research highlighted risks from older vulnerable boot components in configurations that still trust them. In particular, installing a newer boot manager does not necessarily revoke an older signed version. Therefore, version enforcement and revocation are distinct from ordinary patch installation. See MSRC — CVE-2023-21563 and Microsoft KB5025885 — Secure Boot revocation guidance.

Historical CVE-2023-21563 analysis highlights physical access, vulnerable boot components and potential key exposure on affected Windows configurations. Apply applicable revocations, restrict legacy boot paths and secure UEFI administration. Validate recovery media before enforcement; remote attestation can supplement integrity monitoring.

Evil Maid attacks

An unattended device can be altered before its owner returns. For example, a compromised boot path could attempt to capture later authentication input. Secure Boot, measured boot, physical custody and tamper evidence reduce selected risks. However, none alone guarantees integrity against every physical adversary.

Secure Boot certificate expiration and BitLocker in 2026

Microsoft is transitioning from its 2011 Secure Boot certificate hierarchy to replacement certificates issued in 2023. This transition affects boot trust rather than AES encryption keys.

Legacy certificate Expiration period
Microsoft Corporation KEK CA 2011 June 2026
Microsoft UEFI CA 2011 June 2026
Microsoft Windows Production PCA 2011 October 2026

Operational continuity and recovery

Expiration does not automatically decrypt a volume or prevent a previously working machine from booting. Nevertheless, systems that fail to receive updated trust material may lose access to future boot protections. Administrators should inventory firmware compatibility, recovery credentials, Secure Boot trust databases and revocation status. Before deploying revocations, test recovery media and maintain a supported recovery path.

Official guidance: Microsoft — Secure Boot certificate expiration and CA updates and Microsoft KB5025885 — Secure Boot revocation guidance.

Scientific research: the hardware isolation gap in BitLocker forensics

The review The Hardware Isolation Gap: A Systematic Survey of BitLocker Forensics in the TPM 2.0 Era, published on 6 May 2026 in Electronics, examines research from 2006 to 2025. It provides a useful synthesis of changing forensic access opportunities as BitLocker became more closely integrated with platform hardware.

How to interpret forensic evidence

Compare the device state, TPM implementation, protector, firmware, attacker access and evidence-acquisition method before generalising any result. In particular, reported success rates in a research corpus are not universal probabilities for real-world devices. Furthermore, a survey is not an independent reproduction of each experiment, and its historical coverage predates subsequent 2026 disclosures.

Reference: Kenchaiah et al. — The Hardware Isolation Gap, Electronics 15(9), 1959 (6 May 2026).

Forensic preservation

In authorised investigations, preserve chain of custody and document the initial power state, encryption status, evidence handling and every state change. A running system and a powered-off encrypted device present different evidentiary risks. Avoid uncontrolled changes that could destroy volatile evidence or trigger recovery.

Self-encrypting SSDs, TCG Opal and Microsoft eDrive

Self-encrypting drives (SEDs) perform cryptographic operations in storage hardware. TCG Opal defines storage security management capabilities, while Microsoft eDrive historically enabled compatible hardware encryption integration. However, a hardware encryption claim does not establish the security of firmware or authentication.

Research disclosed in 2018 and published at IEEE Security and Privacy in 2019 identified serious defects in selected commercial SSDs. The findings also challenged historical BitLocker configurations that delegated encryption to the drive. See Meijer and van Gastel — Self-encrypting deception, IEEE S&P 2019.

Software versus hardware encryption

Mode Trust dependency Verification
Software BitLocker Windows cryptographic implementation and host key handling Check reported encryption method and policy.
Hardware encryption SSD firmware, access enforcement and drive lifecycle Check model, firmware and vendor advisories.

Microsoft subsequently advised reviewing hardware encryption policy. Changing a policy does not necessarily migrate an existing encrypted volume. Therefore, plan any supported migration with backups and recovery validation. See Microsoft ADV180028 — self-encrypting drives.


Credential theft and social engineering

Impersonation of Microsoft or technical support can induce a user to disclose a recovery password or credential. Verify requests independently, train users and report suspicious activity. TPM lockout limits applicable authentication attempts, not disclosure of valid credentials.

BitLocker recovery key sovereignty and lifecycle management

Recovery passwords can also be printed or saved in a protected file or encrypted external drive. The historical article mentioned Azure Key Vault as a possible custom custody service; it is not a standard native BitLocker recovery escrow destination. Any such integration requires separate access controls and recovery validation.

The 48-digit recovery password constitutes an alternative access mechanism. Accordingly, its custody can be as important as the choice of AES key length. Device Encryption may automatically escrow recovery information under supported account or organisational configurations.

Custody model Benefits Risks
Microsoft account Convenient account-based recovery Account compromise or loss of access.
Microsoft Entra ID / AD DS Managed organisational recovery Privileged administrator access and directory compromise.
Offline controlled backup Independent custody Loss, theft or insufficient redundancy.
Separate application encryption Independent confidentiality boundary Additional key lifecycle and plaintext exposure risks.

Offline options include a protected file, removable medium or printed copy. An organisation may separately manage protected escrow through a key-management service such as Azure Key Vault, subject to its own integration and access controls; this is not presented as a native BitLocker backup destination. Separate application encryption is an additional boundary, not a recovery-password custody model.

Recovery lifecycle

Maintain an inventory of recovery identifiers without publishing secrets. Additionally, restrict retrieval, log authorised access, validate backups and rotate exposed recovery protectors through supported procedures. Separate recovery credentials from the device they protect. For organisations, document delegation, revocation and disaster recovery. See Microsoft — BitLocker recovery process.

BitLocker sleep, hibernation and shutdown security

Physical risk changes with the power state. For example, locking the Windows desktop does not relock the system volume. Likewise, sleep or Modern Standby can retain sensitive material in memory.

State Security consideration
Running / locked Volume normally remains unlocked.
Sleep / Modern Standby RAM may retain active keys.
Hibernation Memory state is saved to storage; protection depends on configuration and resume authentication.
Full shutdown Active keys normally cease to be available, subject to residual memory and platform-specific risks.
Fast Startup Hybrid shutdown differs from a full shutdown.

For sensitive travel or unattended equipment, favour a validated shutdown or appropriately protected hibernation policy. Furthermore, assess DMA protection and pre-boot authentication according to the actual platform. Source: Microsoft — BitLocker countermeasures.

BitCracker, GPU password guessing and TPM anti-hammering

GPU acceleration can reduce the cost of testing guesses against certain password-protected encryption metadata. BitCracker is a research example of this attack class. However, password guessing is not equivalent to brute-forcing the full AES key space, and feasibility depends on protector type, entropy and derivation costs. See BitCracker research project.

TPM anti-hammering constrains applicable hardware authorisation attempts. In contrast, offline guessing against extractable password-protected material can have different constraints. Therefore, use suitable high-entropy credentials and do not equate a startup PIN with a disk encryption key. Artificial intelligence may prioritise likely guesses, but it does not eliminate cryptographic search complexity.

Post-quantum security: AES-128, AES-256 and TPM algorithms

Grover’s algorithm provides a theoretical quadratic advantage for ideal unstructured search. Thus, AES-256 offers a larger nominal security margin against quantum key search than AES-128. However, logical circuit depth, error correction and physical resources prevent interpreting this as a practical present-day attack.

Shor’s algorithm instead concerns mathematical problems underlying RSA and elliptic-curve cryptography. Consequently, consider signatures, attestation and key establishment separately from symmetric volume encryption. TPM 2.0 is not inherently a post-quantum specification.

Limits of post-quantum protection

XTS-AES protects storage confidentiality but is not a general authenticated-encryption construction. Moreover, replacing public-key algorithms with PQC cannot repair unsafe recovery authorisation, memory corruption or credential theft. References: NIST FIPS 197 — AES, NIST SP 800-38E — XTS-AES and NIST — Post-Quantum Cryptography.

Permanent BitLocker attack taxonomy and countermeasure matrix

The table separates attack targets from countermeasures. These measures reduce specific risks rather than guaranteeing immunity. No demonstrated mathematical AES break is implied by the listed practical attacks.

Attack family Target / prerequisite Defensive focus
Cold boot / RAM analysis Residual or live memory Power-state policy and physical custody
DMA / Thunderclap Accessible memory via peripherals IOMMU, DMA policy and port control
TPM bus interception Exposed discrete TPM communications Pre-boot authentication and platform assessment
faulTPM Specific firmware TPM implementation Vendor updates and hardware assessment
Fault injection / Intel DCI Physical hardware or debug interface Disable unauthorised debug; hardware assurance
BlackLotus / BitPixie Boot integrity or rollback Revocation and secure version enforcement
BitUnlocker / YellowKey Recovery trust Supported updates, WinRE and protector policy
Evil Maid Unattended device Custody, boot integrity and tamper evidence
Phishing / recovery theft User or escrowed credentials Access governance and education
SSD firmware defects Delegated storage encryption Firmware assurance and software mode assessment
GPU guessing Weak password protector Entropy and protector selection
Quantum search Theoretical cryptographic search Algorithm agility and security margin

Editorial change log and evidence policy

10 February 2024: initial publication, as recorded by the author. 2024–2025: historical revisions preserved in the supplied corpus. 16 November 2026: updated vulnerability review, historical timeline, forensic literature, boot trust, recovery sovereignty, SSD security and quantum analysis.

Historical material has been consolidated into the relevant thematic chapters; outdated technical claims are qualified in context. The reference distinguishes vendor advisories, research reports and editorial analysis. It does not represent a complete vulnerability inventory or independent experimental qualification.

8. Limits, evidence and scope of validity

The November vulnerability descriptions do not establish the exact exploit path, VMK extraction, TPM compromise or the ability to bypass a startup PIN. CVSS ratings describe standardised impact and prerequisites; physical exposure must be evaluated in context.

This publication does not claim independent reproduction of the 2026 vulnerabilities, universal resistance of complementary products, or certification of any device configuration.

9. Conclusion

Overall, BitLocker remains a useful defence for data at rest. Its security must be evaluated across the complete authorisation and recovery chain. Maintaining supported software, securing pre-boot authentication and recovery credentials, and applying independent encryption where justified provide complementary layers of protection.

Breaking an encryption algorithm is not necessary when the mechanism that authorizes decryption can be compromised.

11. Technical glossary

AESDefinition
Advanced Encryption Standard.
XTS-AESDefinition
Storage encryption mode designed for data units on disks.
TPMDefinition
Trusted Platform Module: protected cryptographic operations and platform measurements.
PCRDefinition
Platform Configuration Register: records measured state.
VMKDefinition
Volume Master Key: protects the FVEK.
FVEKDefinition
Full Volume Encryption Key: encrypts volume data.
WinREDefinition
Windows Recovery Environment.
DMADefinition
Direct Memory Access.
CVSSDefinition
Common Vulnerability Scoring System.
HSMDefinition
Hardware Security Module.
PQCDefinition
Post-quantum cryptography.
TCBDefinition
Trusted Computing Base: components on which a security property depends.
REVISEDefinition
Secure version enforcement for critical boot components.
DBXDefinition
UEFI Secure Boot forbidden signature database.
SEDDefinition
Self-encrypting drive.
IOMMUDefinition
Input/output memory management unit, used to constrain DMA.
SRTMDefinition
Static Root of Trust for Measurement.
SVNDefinition
Security version number used in rollback prevention.
EscrowDefinition
Controlled custody of recovery information.
GroverDefinition
Quantum algorithm providing a theoretical quadratic search advantage.

12. Frequently asked questions about BitLocker security

CVE-2026-97015 and CVE-2026-119832 are physical security bypass vulnerabilities disclosed November 10.

No cryptographic break of AES is established by these disclosures.

CVE-2026-45585 is a publicly disclosed security bypass. Consult the Microsoft advisory.

Generally no. Apply security updates and verify protection instead.

No. It mitigates selected pre-boot risks.

Yes, provided independent keys and plaintext remain inaccessible to the attacker.

BitLocker is an encryption feature included in Microsoft Windows. It protects your data by encrypting the entire disk, making the protected volume unreadable without valid unlocking material. See the architecture chapter for TPM and key protectors.

BitLocker can encrypt internal hard drives, external USB drives (using BitLocker To Go), and even virtual hard drives (VHD). It is a versatile solution for securing various types of storage.

Eligible Windows Home devices may support Device Encryption.

Performance varies with workload and hardware. AES-NI acceleration can reduce overhead.

To activate BitLocker on Windows 11, go to Settings > Privacy & Security > Device Encryption. If the option isn’t available, search for Manage BitLocker in the Control Panel. Follow the instructions to enable BitLocker on the desired drive.

To deactivate BitLocker, navigate to Settings > Privacy & Security > Device Encryption > Manage BitLocker. Select the drive you want to decrypt and choose Turn off BitLocker. Keep in mind that this process will decrypt your data and may take some time.

Automatic encryption depends on device eligibility and setup/account conditions.

BitLocker may request a recovery key if a Windows update changes the system configuration or boot files. To prevent this, ensure that you save your recovery key securely and update your firmware and drivers.

You can retrieve your BitLocker recovery key from:

Your Microsoft account (if backed up there)

A USB flash drive (if you saved it there)

A printed copy you stored securely

Your organisation’s IT department if using a company-managed device

There is no supported universal recovery bypass; vulnerabilities can nevertheless bypass protection in specific configurations.

Ensure you have the correct recovery key. If the drive is inaccessible, you may use BitLocker repair tools like the repair-bde command in Windows to attempt data recovery.

BIOS updates or hardware changes can trigger BitLocker recovery mode. Ensure you have your recovery key before making such changes. Afterward, re-enable BitLocker to restore normal functionality.

BitLocker primarily uses AES (Advanced Encryption Standard) with 128-bit or 256-bit key lengths, depending on your configuration. AES-256 offers stronger encryption for highly sensitive data.

BitLocker protects data from unauthorised access but does not prevent malware infections. Use antivirus software alongside BitLocker for comprehensive protection.

Yes, BitLocker supports multi-factor authentication by combining a TPM with a PIN or a startup key on a USB drive.

Encryption supports compliance but does not by itself establish GDPR compliance.

BitLocker encrypts data using AES, which prevents unauthorised access even if the physical drive is removed. With a TPM and PIN, the encryption key remains secure.

Yes, BitLocker can be used without a TPM by enabling the “Allow BitLocker without a compatible TPM” policy and using a password or USB startup key for authentication.

No, BitLocker is a Windows-exclusive feature. However, tools like Dislocker can be used on Linux or Mac to access BitLocker-encrypted drives.

To use BitLocker, you need:

A compatible version of Windows (Pro, Enterprise, or Education)

A TPM 1.2 or 2.0 chip (optional)

A modern processor with encryption acceleration for optimal performance

Yes, BitLocker To Go is specifically designed to encrypt external drives like USB sticks and portable hard drives.

Recent vulnerabilities include:

CVE-2023-1017 and CVE-2023-1018 affecting TPM 2.0

Risks from physical attacks like Cold Boot or Bus Pirate attacks

Ensure regular firmware updates and use multi-factor authentication to mitigate these risks.

If no valid protector remains available, there is no supported universal recovery method. Maintain independent, verified backups.

Updates for these vulnerabilities include TPM firmware patches that address buffer overflow risks. Regularly updating your TPM firmware ensures protection against these and other emerging threats.

Updating your TPM firmware helps mitigate recent vulnerabilities like CVE-2023-1017 and CVE-2023-1018, ensuring your device maintains optimal security against physical and software-based attacks.

External credential storage does not guarantee that input is never exposed on a compromised host.

The historical product description specifies AES-256 credential encryption and NFC-enabled access. Protection after device loss depends on the deployed pairing, authentication and key custody controls. See the product analysis.

Yes, PassCypher is designed to work seamlessly with tools like DataShielder and EviCypher, creating a comprehensive security ecosystem for protecting sensitive data.

DataShielder provides a separate AES-256 encryption layer under independent key custody. See the architectural analysis and limitations.

Independent keys and plaintext may still be exposed during active processing depending on implementation.

Yes, DataShielder supports encryption for external drives, adding an additional layer of security to portable storage devices encrypted with BitLocker.

Yes. An older trusted boot component may restore a vulnerable path unless applicable revocations and version enforcement are deployed.
Not automatically. Nevertheless, outdated trust material can restrict future boot security updates.
No. Its security depends on the actual drive firmware and authentication implementation.
Not necessarily. A locked session usually leaves the operating system volume unlocked.
No practical quantum break is established here. AES-256 offers a greater theoretical search margin; public-key migration is a separate issue.
The authorised owner or organisation should select a custody model, restrict access and validate recovery backups.

How the attack against Microsoft Exchange on December 13, 2023 exposed thousands of email accounts

Digital shield by Freemindtronic repelling cyberattack against Microsoft Exchange

How to protect yourself from the attack against Microsoft Exchange?

The attack against Microsoft Exchange was a serious security breach in 2023. Thousands of organizations worldwide were hacked by cybercriminals who exploited vulnerabilities in Microsoft’s email servers. How did this happen? What were the consequences? How did Microsoft react? And most importantly, how can you protect your data and communications? Read our comprehensive analysis and discover Freemindtronic’s technology solutions.

Cyberattack against Microsoft: discover the potential dangers of stalkerware spyware, one of the attack vectors used by hackers. Stay informed by browsing our constantly updated topics.

[bws_pdfprint display=’print’]Cyberattack against Microsoft: How to Protect Yourself from Stalkerware, a book by Jacques Gascuel, the innovator behind advanced sensitive data security and safety systems, provides invaluable knowledge on how data encryption and decryption can prevent email compromise and other threats.

How the attack against Microsoft Exchange on December 13, 2023 exposed thousands of email accounts

On December 13, 2023, Microsoft was the target of a sophisticated attack by a hacker group called Lapsus$. This attack exploited another vulnerability in Microsoft Exchange, known as CVE-2023-23415, which allowed the attackers to execute remote code on the email servers using the ICMP protocol. The attackers were able to access the email accounts of more than 10,000 Microsoft employees, some of whom were working on sensitive projects such as the development of GTA VI or the launch of Windows 12. The attackers also published part of the stolen data on a website called DarkBeam, where they sold more than 750 million fraudulent Microsoft accounts. Microsoft reacted quickly by releasing a security patch on December 15, 2023, and collaborating with the authorities to arrest the perpetrators of the attack. One of the members of the Lapsus$ group, an Albanian hacker named Kurtaj, was arrested on December 20, 2023, thanks to the cooperation between the American and European intelligence services1234.

What were the objectives and consequences of the attack?

The attack against Microsoft Exchange affected more than 20,000 email servers worldwide, belonging to businesses, institutions and organizations from different sectors. These servers were vulnerable because they used outdated versions of the software, which no longer received security updates. The attack exploited a critical vulnerability known as ProxyLogon (CVE-2023-23415), allowing the attackers to execute remote code on the servers and access the email accounts. Despite the efforts to solve the problem, many vulnerable servers remained active, exposing the email accounts of about 30,000 high-level employees, including executives and engineers. The attackers were able to steal confidential information, such as internal projects, development plans, trade secrets or source codes.

What were the objectives of the attack?

The attack was attributed to Lapsus$, a hacker group linked to Russia. According to Microsoft, the group’s main objective was to gain access to sensitive information from various targets, such as government agencies, think tanks, NGOs, law firms, medical institutions, etc. The group also aimed to compromise the security and reputation of Microsoft, one of the leading technology companies in the world. The attack was part of a larger campaign that also involved the SolarWinds hack, which affected thousands of organizations in 2020.

What were the impacts of the attack?

The attack had serious impacts on the victims, both in terms of data loss and reputation damage. The data stolen by the attackers included personal and professional information, such as names, addresses, phone numbers, email addresses, passwords, bank details, credit card numbers, health records, etc. The attackers also leaked some of the data on the DarkBeam website, where they offered to sell the data to the highest bidder. This exposed the victims to potential identity theft, fraud, blackmail, extortion, or other cybercrimes. The attack also damaged the reputation of Microsoft and its customers, who were seen as vulnerable and unreliable by their partners, clients, and users. The attack also raised questions about the security and privacy of email communication, which is widely used in the digital world.

What were the consequences of the attack?

The attack had several consequences for Microsoft and its customers, who had to take urgent measures to mitigate the damage and prevent further attacks. Microsoft had to release a security patch for the vulnerability, and urge its customers to update their software as soon as possible. Microsoft also had to investigate the origin and extent of the attack, and cooperate with the authorities to identify and arrest the attackers. Microsoft also had to provide support and assistance to its customers, who had to deal with the aftermath of the attack. The customers had to check their email accounts for any signs of compromise, and change their passwords and security settings. They also had to notify their contacts, partners, and clients about the breach, and reassure them about the security of their data. They also had to monitor their online activities and accounts for any suspicious or fraudulent transactions. The attack also forced Microsoft and its customers to review and improve their security policies and practices, and adopt new solutions and technologies to protect their data and communication.

How did the attack succeed despite Microsoft’s defenses?

The attack was sophisticated and stealthy, using several techniques to bypass Microsoft’s defenses. First, the attackers exploited a zero-day vulnerability, which means that it was unknown to Microsoft and the public until it was discovered and reported. Second, the attackers used a proxy tool to disguise their origin and avoid detection. Third, the attackers used web shells to maintain persistent access to the servers and execute commands remotely. Fourth, the attackers used encryption and obfuscation to hide their malicious code and data. Fifth, the attackers targeted specific servers and accounts, rather than launching a massive attack that would have raised more suspicion.

What are the communication vulnerabilities exploited by the attack?

The attack exploited several communication vulnerabilities, such as:

  • Targeted phishing: The attackers sent fake emails to the victims, pretending to be from legitimate sources, such as Microsoft, their bank, or their employer. The emails contained malicious links or attachments, that led the victims to compromised websites or downloaded malware on their devices. The attackers then used the malware to access the email servers and accounts.
  • SolarWinds exploitation: The attackers also used the SolarWinds hack, which was a massive cyberattack that compromised the software company SolarWinds and its customers, including Microsoft. The attackers inserted a backdoor in the SolarWinds software, which allowed them to access the networks and systems of the customers who installed the software. The attackers then used the backdoor to access the email servers and accounts.
  • Brute force attack: The attackers also used a brute force attack, which is a trial-and-error method to guess the passwords or encryption keys of the email accounts. The attackers used automated tools to generate and test a large number of possible combinations, until they found the right one. The attackers then used the passwords or keys to access the email accounts.
  • SQL injection: The attackers also used a SQL injection, which is a technique to insert malicious SQL commands into a web application that interacts with a database. The attackers used the SQL commands to manipulate the database, and access or modify the data stored in it. The attackers then used the data to access the email accounts.

Why did the detection and defense systems of Microsoft Exchange not work?

The detection and defense systems of Microsoft Exchange did not work because the attackers used advanced techniques to evade them. For example, the attackers used a proxy tool to hide their IP address and location, and avoid being traced or blocked by firewalls or antivirus software. The attackers also used web shells to create a backdoor on the servers, and execute commands remotely, without being noticed by the system administrators or the security software. The attackers also used encryption and obfuscation to conceal their malicious code and data, and prevent them from being analyzed or detected by the security software. The attackers also used zero-day vulnerability, which was not known or patched by Microsoft, and therefore not protected by the security software.

How did Microsoft react to the attack?

Microsoft reacted to the attack by taking several actions, such as:

The main actions of Microsoft

  • Releasing a security patch: Microsoft released a security patch for the vulnerability exploited by the attack, and urged its customers to update their software as soon as possible. The patch fixed the vulnerability and prevented further attacks.
  • Investigating the attack: Microsoft investigated the origin and extent of the attack, and collected evidence and information about the attackers and their methods. Microsoft also cooperated with the authorities and other organizations to identify and arrest the attackers.
  • Providing support and assistance: Microsoft provided support and assistance to its customers, who were affected by the attack. Microsoft offered guidance and tools to help the customers check their email accounts for any signs of compromise, and change their passwords and security settings. Microsoft also offered free credit monitoring and identity theft protection services to the customers, who had their personal and financial data stolen by the attackers.

Microsoft also released patches for the vulnerabilities exploited by the attack

Microsoft also released patches for the other vulnerabilities exploited by the attack, such as the SolarWinds vulnerability, the brute force vulnerability, and the SQL injection vulnerability. Microsoft also improved its detection and defense systems, and added new features and functions to its software, to enhance the security and privacy of email communication.

What are the lessons to be learned from the attack?

The attack was a wake-up call for Microsoft and its customers, who had to learn from their mistakes and improve their security practices. Some of the lessons to be learned from the attack are:

Email security

Email is one of the most widely used communication tools in the digital world, but also one of the most vulnerable to cyberattacks. Therefore, it is essential to ensure the security and privacy of email communication, by applying some best practices, such as:

  • Using strong and unique passwords for each email account, and changing them regularly.
  • Using multi-factor authentication (MFA) to verify the identity of the email users, and prevent unauthorized access.
  • Using encryption to protect the content and attachments of the email messages, and prevent them from being read or modified by third parties.
  • Using digital signatures to verify the authenticity and integrity of the email messages, and prevent them from being spoofed or tampered with.
  • Using spam filters and antivirus software to block and remove malicious emails, and avoid clicking on suspicious links or attachments.
  • Using secure email providers and platforms, that comply with the latest security standards and regulations, and offer features such as end-to-end encryption, zero-knowledge encryption, or self-destructing messages.

Multi-factor authentication

Multi-factor authentication (MFA) is a security method that requires the user to provide two or more pieces of evidence to prove their identity, before accessing a system or a service. The pieces of evidence can be something the user knows (such as a password or a PIN), something the user has (such as a smartphone or a token), or something the user is (such as a fingerprint or a face scan). MFA can prevent unauthorized access to email accounts, even if the password is compromised, by adding an extra layer of security. Therefore, it is recommended to enable MFA for all email accounts, and use reliable and secure methods, such as biometric authentication, one-time passwords, or push notifications.

Principle of least privilege

The principle of least privilege (POLP) is a security concept that states that each user or system should have the minimum level of access or permissions required to perform their tasks, and nothing more. POLP can reduce the risk of data breaches, by limiting the exposure and impact of a potential attack. Therefore, it is advisable to apply POLP to email accounts, and assign different roles and privileges to different users, depending on their needs and responsibilities. For example, only authorized users should have access to sensitive or confidential information, and only administrators should have access to system settings or configuration.

Software update

Software update is a process that involves installing the latest versions or patches of the software, to fix bugs, improve performance, or add new features. Software update is crucial for email security, as it can prevent the exploitation of vulnerabilities that could allow attackers to access or compromise the email servers or accounts. Therefore, it is important to update the software regularly, and install the security patches as soon as they are available. It is also important to update the software of the devices that are used to access the email accounts, such as computers or smartphones, and use the latest versions of the browsers or the applications.

System monitoring

System monitoring is a process that involves observing and analyzing the activity and performance of the system, to detect and resolve any issues or anomalies. System monitoring is vital for email security, as it can help to identify and stop any potential attacks, before they cause any damage or disruption. Therefore, it is essential to monitor the email servers and accounts, and use tools and techniques, such as logs, alerts, reports, or audits, to collect and analyze the data. It is also essential to monitor the email traffic and behavior, and use tools and techniques, such as firewalls, intrusion detection systems, or anomaly detection systems, to filter and block any malicious or suspicious activity.

User awareness

User awareness is a state of knowledge and understanding of the users, regarding the security risks and threats that they may face, and the best practices and policies that they should follow, to protect themselves and the system. User awareness is key for email security, as it can prevent many human errors or mistakes, that could compromise the email accounts or expose the data. Therefore, it is important to educate and train the email users, and provide them with the necessary information and guidance, to help them recognize and avoid any phishing, malware, or social engineering attacks, that could target their email accounts.

What are the best practices to strengthen information security?

Information security is the practice of protecting the confidentiality, integrity, and availability of the information, from unauthorized or malicious access, use, modification, or destruction. Information security is essential for email communication, as it can ensure the protection and privacy of the data and messages that are exchanged. Some of the best practices to strengthen information security are:

  • Adopt the Zero Trust model: The Zero Trust model is a security approach that assumes that no user or system can be trusted by default, and that each request or transaction must be verified and authorized, before granting access or permission. The Zero Trust model can enhance information security, by reducing the attack surface and preventing the lateral movement of the attackers, within the system.
  • Use advanced protection solutions: Advanced protection solutions are security solutions that use artificial intelligence, machine learning, or other technologies, to detect and respond to the most sophisticated and complex cyberattacks, that could target the email accounts or data. Some of these solutions are endpoint detection and response (EDR), identity and access management (IAM), or data encryption solutions.
  • Hire cybersecurity experts: Cybersecurity experts are professionals who have the skills and knowledge to design, implement, and maintain the security of the system and the information, and to prevent, detect, and respond to any cyberattacks, that could affect the email accounts or data. Cybersecurity experts can help to strengthen information security, by providing advice, guidance, and support, to the email users and administrators.

How can Freemindtronic technology help to fight against this type of attack?

Freemindtronic offers innovative and effective technology solutions such as EviCypher NFC HSM and EviPass NFC HSM and EviOTP NFC HSM and other PGP HSMs. They can help businesses to fight against this type of attack based on Zero Day and other threats. Their technology is embedded in products such as DataShielder NFC HSM and DataShielder HSM PGP and DataShielder Defense or PassCypher NFC HSM or PassCypher HSM PGP. These products provide security and communication features for data, email and password management and offline OTP secret keys.

  • DataShielder NFC HSM is a portable device that allows to encrypt and decrypt data and communication on a computer or on an Android NFC smartphone. It uses a contactless hardware security module (HSM) that generates and stores encryption keys securely and segmented. It protects the keys that encrypt contactless communication. This has the effect of effectively fighting against all types of communication vulnerabilities, since the messages and attachments will remain encrypted even if they are corrupted. This function regardless of where the attack comes from, internal or external to the company. It is a counter-espionage solution. It also offers other features, such as password management, 2FA – OTP (TOTP and HOTP) secret keys. In addition, DataShielder works offline, without server and without database. It has a configurable multi-authentication system, strong authentication and secure key sharing.
  • DataShielder HSM PGP is an application that transforms all types of physical storage media (USB key, S, SSD, KeyChain / KeyStore) connected or not connected into HSM. It has the same features as its NFC HSM version. However, it also uses standard AES-256 and RSA 4096 algorithms, as well as OpenPGP algorithms. It uses its HSMs to manage and store PGP keys securely. In the same way, it protects email against phishing and other email threats. It also offers other features, such as digital signature, identity verification or secure key sharing.
  • DataShielder Defense is a dual-use platform for civilian and military use that offers many functions including all those previously mentioned. It also works in real time without server, without database from any type of HSM including NFC. It also has functions to add trust criteria to fight against identity theft. It protects data and communication against cyberattacks and data breaches.

In summary

To safeguard against the Microsoft Exchange attack, prioritize security updates and patches. Embrace Freemindtronic’s innovative solutions for enhanced protection. Stay vigilant against phishing and employ robust authentication methods. Opt for encryption to shield communications. Engage cybersecurity experts for advanced defense strategies. By adopting these measures, you can fortify your defenses against cyber threats and ensure your data’s safety.

Ivanti Zero-Day Flaws: Comprehensive Guide to Secure Your Systems Now

Digital representation of Ivanti Zero-Day Flaws threatening cybersecurity in a futuristic cityscape

Ivanti Patches Two Critical Zero-Day Vulnerabilities, One Under Active Attack

Ivanti, a leader in endpoint and network management solutions, has patched two critical zero-day vulnerabilities, one of which was actively exploited by cybercriminals. Learn more about these vulnerabilities and how to protect your organization.

This sentence is under a slider that shows similar topics on the zero day.

[bws_pdfprint display=’print’]The Ivanti zero-day flaws, written by Jacques Gascuel, inventor of cybersecurity solutions, of cyber-safety of sensitive data and of counter-espionage, deal with the subject of the Ivanti Zero Day 2024 vulnerabilities.

What are Zero-Day Flaws and Why are They Dangerous?

A zero-day flaw is a previously unknown vulnerability in software that hackers can exploit before the vendor becomes aware and devises a patch. These vulnerabilities are particularly perilous because there is no existing defense against their exploitation. Cybercriminals can use zero-day flaws to launch sophisticated cyberattacks, leading to unauthorized data access, system damage, and widespread security breaches.

Ivanti’s Two Zero-Day Vulnerabilities: CVE-2024-21888 and CVE-2024-21893

Ivanti’s announcement highlights two specific vulnerabilities:

  • CVE-2024-21888: This is a critical privilege escalation vulnerability found in the web components of Ivanti Connect Secure and Policy Secure (versions 9.x, 22.x). It allows malicious users to gain administrator privileges, thereby obtaining the ability to alter system configurations, access restricted data, and potentially introduce further malicious code into the network infrastructure.
  • CVE-2024-21893: Identified as a server-side request forgery (SSRF) flaw within the SAML component of Ivanti Connect Secure, Policy Secure (versions 9.x, 22.x), and Ivanti Neurons for ZTA, this vulnerability enables attackers to bypass authentication mechanisms to access restricted resources. This flaw is particularly concerning due to its active exploitation, which suggests a targeted approach by cybercriminals to leverage this vulnerability for malicious purposes.

Ivanti has acknowledged the targeted exploitation of CVE-2024-21893 and expressed concerns over the potential for increased malicious activities following the public disclosure of these vulnerabilities.

How to Protect Your Organization from Ivanti’s Zero-Day Flaws

In response to the discovery of these vulnerabilities, Ivanti has taken swift action by releasing patches for the affected products, including specific versions of Connect Secure and ZTA. The company strongly advises a precautionary factory reset of devices before applying the patches to eliminate any lingering threats from the system. Additionally, Ivanti recommends importing a mitigation file named “mitigation.release.20240126.5.xml” as a temporary countermeasure against these vulnerabilities.

To safeguard against these vulnerabilities, organizations are urged to apply Ivanti’s patches immediately, conduct a factory reset of devices prior to patching, and adopt a proactive cybersecurity posture. This includes regular software updates, comprehensive user education on cybersecurity best practices, and the implementation of robust security measures such as firewalls, intrusion detection systems, and regular security audits.

The Impact of Ivanti’s Zero-Day Flaws on the Cybersecurity Landscape

Since the beginning of 2024, the cybersecurity community has witnessed the disclosure of six zero-day vulnerabilities within Ivanti’s product lineup, with half of them being actively exploited. A study conducted by Volexity found that more than 1,700 Ivanti devices have been compromised worldwide, including nearly 100 in France. These attacks have affected organizations from all sectors, including government agencies, Fortune 500 companies and cloud service providers .

CISA Issues Emergency Directive for Federal Agencies

The US Cybersecurity and Infrastructure Security Agency (CISA) issued an emergency directive. It requires all federal agencies to apply Ivanti’s patches and mitigations, and report any compromise to the CISA. This directive is important because it shows the urgency and the severity of the situation, and its implications for the national and international security.

Mandiant Identifies Bypass Technique and Webshell Deployment

Mandiant, a cybersecurity firm, has identified a technique that bypasses the mitigation file and allows the deployment of a custom webshell named BUSHWALK. This webshell works by injecting malicious code into the legitimate web pages of Ivanti devices, and allows the attackers to execute commands and access files on the compromised systems. Mandiant has provided a detailed description of how this webshell works, how to detect it, and how to remove it. Mandiant has also clarified that this technique is distinct from the mass exploitation that followed the disclosure of the vulnerabilities.

UNC5221: The Threat Group Behind the Targeted Exploitation

Mandiant has also attributed the exploitation of the Ivanti zero-day flaws to a threat group named UNC5221, suspected to be linked to China. This group has targeted organizations from various sectors, including government agencies, Fortune 500 companies and cloud service providers . Mandiant has also revealed the tools and the malware used by this group, such as BUSHWALK, BLOODHOUND, CHOPSTICK and SLIGHTPULSE. These tools and malware are designed to perform reconnaissance, lateral movement, credential theft and data exfiltration on the compromised networks.

The Number of Victims and the Potential Consequences

According to the latest reports from Volexity and Mandiant, more than 1,700 Ivanti devices have been compromised worldwide, including nearly 100 in France. The sectors most affected by these intrusions include government, finance, healthcare, education, and technology. The potential consequences of these intrusions include unauthorized data access, system encryption by ransomware, installation of backdoors for persistent access, and execution of malicious code. Such incidents can lead to significant financial losses, reputational damage, operational disruptions, and legal implications for the affected organizations.

EviCypher and EviPass: Innovative Technologies to Protect Yourself from the Zero-Day Flaws

Facing the threat of the Ivanti zero-day flaws, there are innovative solutions to protect yourself effectively. These are the EviCypher and EviPass technologies, developed by Freemindtronic, a company specialized in pocket cybersecurity.

EviCypher is a NFC device that allows you to encrypt and decrypt messages securely and anonymously. You just need to slide your EviCypher card behind your smartphone for the message to be encrypted or decrypted. The system uses individual encryption keys, stored offline, in a non-volatile and physically secure memory. Thus, even if the message is intercepted by an attacker who exploits an Ivanti zero-day flaw, he will not be able to read it without the corresponding key.

EviPass is a mobile application that allows you to manage your passwords and credentials securely and conveniently. You just need to scan your EviPass card with your smartphone to access your online accounts. The application uses an OpenPGP encryption algorithm, based on public and private keys. The private keys are stored offline, in a non-volatile and physically secure memory. Thus, even if an attacker manages to access a compromised Ivanti device, he will not be able to steal the passwords and credentials without the EviPass card.

These two solutions offer a high level of security, based on the principle of “Air Gap”, which consists of creating a physical and digital barrier between the data and the attackers. They are also easy to use, without requiring any specific knowledge in cybersecurity. They are compatible with all digital communication systems, including those that use Ivanti products. They are protected by international patents, and manufactured in Andorra by Freemindtronic.

EviPass NFC NFC and EviPass HSM PGP: Freemindtronic’s Technologies for Password Management

EviPass NFC NFC and EviPass HSM PGP are two technologies developed by Freemindtronic for password management. EviPass NFC NFC is a technology that uses NFC cards to store and access passwords and credentials. EviPass HSM PGP is a technology that uses hardware security modules (HSM) to store and access passwords and credentials using the OpenPGP encryption algorithm. Both technologies are integrated into the EviPass mobile application, which allows users to manage their passwords and credentials securely and conveniently.

EviCypher NFC HSM and EviCypher HSM PGP: Freemindtronic’s Technologies for Message Encryption

EviCypher NFC HSM and EviCypher HSM PGP are two technologies developed by Freemindtronic for message encryption. EviCypher NFC HSM is a technology that uses NFC cards and hardware security modules (HSM) to encrypt and decrypt messages. EviCypher HSM PGP is a technology that uses hardware security modules (HSM) to encrypt and decrypt messages using the OpenPGP encryption algorithm. Both technologies are integrated into the EviCypher NFC device, which allows users to encrypt and decrypt messages securely and anonymously.

PassCypher and DataShielder: Freemindtronic’s Products that Incorporate EviCypher and EviPass Technologies

PassCypher and DataShielder are two products designed and manufactured by Freemindtronic that incorporate the EviCypher and EviPass technologies. PassCypher is a NFC device that connects to your smartphone or computer and allows you to access your online accounts using the EviPass technology. DataShielder is a NFC device that connects to your smartphone or computer and allows you to encrypt and decrypt messages using the EviCypher technology. With these products, you can benefit from the EviCypher and EviPass technology to protect your passwords, credentials and messages.

To learn more about these solutions, you can visit the Freemindtronic website or the Codeur blog, which present the features and benefits of EviCypher and EviPass.

Conclusion

In conclusion, the Ivanti zero-day flaws are dangerous vulnerabilities that can compromise the security and confidentiality of the users’ data. It is therefore important to protect yourself effectively against these flaws, by applying the patches provided by Ivanti, following the cybersecurity recommendations, and using innovative solutions like EviCypher and EviPass, developed by Freemindtronic. These solutions are integrated into innovative products, designed and manufactured in Andorra. Don’t wait any longer to protect yourself from the Ivanti zero-day flaws, and discover the EviCypher and EviPass solutions from Freemindtronic. What are your impressions on these products? Let us know in the comments below.

How to protect yourself from stalkerware on any phone

Woman holding a smartphone with a padlock icon on the screen, promoting protection from stalkerware.

How to Protect Yourself from Stalkerware

How to protect yourself from stalkerware: In today’s digital landscape, being mindful of stalkerware’s escalating threat is crucial. Take proactive measures to safeguard your privacy. Stalkerware, a malware type, lets unauthorized individuals stealthily monitor and control your smartphone.

To learn more about the potential dangers of stalkerware spyware.” Stay informed by browsing our constantly updated topics

[bws_pdfprint display=’print’]How to Protect Yourself from Stalkerware written by Jacques Gascuel, the innovator behind advanced sensitive data security and safety systems, provides priceless knowledge on the topic of data encryption and decryption. Are you prepared to enhance your comprehension of data protection?

What is Stalkerware and Why is it Dangerous?

Stalkerware, including known programs like FlexiSpy, mSpy, and Spyera, tracks your location and accesses calls, messages, and photos. These programs can secretly activate your camera or microphone. To counter these invasions, safeguard your digital privacy from stalkerware. Physical access or being tricked into clicking malicious links; often in phishing emails, leads to stalkerware installation.

Who Uses Stalkerware?

Furthermore, abusive partners, stalkers, employers, or governments often use stalkerware. They exploit tools like FlexiSpy or Spyera to gain unauthorized access to personal information, track whereabouts, or monitor online activities.

How to Detect and Remove Stalkerware from Your Phone

To detect stalkerware, check for unusual apps or files. Monitor your phone bill for spikes in data usage or unexpected charges. Be cautious about what you click on, and keep your phone and apps updated. Consider well-known antivirus or security apps like Malwarebytes; Kaspersky Internet Security for added protection.

Signs of Stalkerware Infection

To detect stalkerware, you can follow these steps:

  • Check for unusual apps or files: If you notice any unfamiliar apps or files on your phone, it could be a sign that stalkerware is installed. Be sure to check the permissions for any apps you don’t recognize and uninstall any that seem suspicious.
  • Monitor your phone bill: Unusual spikes in data usage or unexpected charges could signal stalkerware installation. Contact your phone carrier to investigate.
  • Be cautious about what you click on: Don’t click on links or open attachments from unknown senders, as these could be used to install stalkerware on your phone.
  • Keep your phone and apps updated: Make sure your phone’s operating system and apps are up to date with the latest security patches. These updates often include fixes for vulnerabilities that could be exploited by stalkerware or other malware.
  • Use a reputable antivirus or security app: Antivirus and security apps can help to detect and remove stalkerware, as well as protect you from other types of malware.

In case you suspect the presence of stalkerware on your phone, you may attempt to remove it using one of the aforementioned methods. However, if you are not comfortable doing this yourself, you can take your phone to a professional for help.

Steps to Remove Stalkerware

  • Backup your data first
  • Perform a factory reset on your device
  • Change all your passwords post-reset

Protecting Sensitive Data from Stalkerware

Fortifying Sensitive Data with Freemindtronic’s Solutions

In the battle against stalkerware, safeguarding your sensitive data is paramount. Freemindtronic, an innovative Andorran cybersecurity company, offers cutting-edge solutions that not only protect your privacy but also fortify your data against prying eyes. Leveraging contactless encryption through an NFC hardware security module (HSM) and other secure storage media, these solutions make your secrets virtually inaccessible to tracking software.

EviCypher NFC HSM This module secures encryption keys from an externalized source, ensuring the protection of data on NFC devices. Its robust security shields against stalkerware and other cyber threats.

EviCypher HSM OpenPGP: Versatile and adaptable, it creates an HSM across various storage types, supporting keychains, keystores, SD, and USB OTG keys. Compliant with encryption standards and the OpenPGP encryption standard, it safeguards a wide array of sensitive data, including emails, documents, and photos.

EviPass: A hardware password manager that securely stores your passwords within a tamper-proof device, making it exceedingly difficult, if not impossible, for tracking software to pilfer your passwords from an NFC HSM or HSM PGP.

EviOTP: This OTP token manager, housed within an NFC HSM or HSM PGP, generates one-time passwords (TOTP or HOTP) for two-factor authentication. This additional layer of physical security thwarts token exploitation, fortifying the protection of your online accounts.

Seamless Integration Across Product Lines

Freemindtronic solutions provide an additional layer of defense against spyware and seamlessly integrate into various products.

Integration of Password Manager Technology

For instance, EviPasse HSM HSP, an advanced password manager technology, integrates seamlessly into the PassCypher HSM PGP product. It ensures the security of identification and authentication secrets in computer systems.

Enhanced NFC Security

Similarly, EviPass NFC HSM technology seamlessly embeds into the PassCypher NFC HSM product, securing NFC Android phones via NFC HSM.

Strengthening Authentication Security

Moreover, PassCypher NFC HSM takes it a step further by incorporating EviOTP technology to bolster the security of 2FA double authentication tokens on phones and computers.

Data Encryption Without Contact

EviCypher NFC HSM technology plays a vital role as an encryption key manager in DataShielder NFC HSM products. It enables users to encrypt sensitive email, SMS, MMS, and RCS data without contact. This offers effective protection against spyware like Stalkerware. Users physically outsource secrets from their phones or computers, ensuring data security against cyber threats.

Cornerstone of Data Security

As for EviCypher HSM PGP technology, it serves as the cornerstone of the DataShielder HSM PGP product on computer systems. It is also compatible with DataShielder NFC HSM. This simultaneous security ensures sensitive information on both phones and computers.

Comprehensive Security Suite

Finally, for ultimate versatility and mobility, DataShielder Defense, designed for civil and military use, encompasses these technologies and many others. This comprehensive suite strengthens data protection against physical and software espionage, identity theft, corruption of sensitive data, illicit extraction of secrets, and other threats. Thanks to its interoperability and backward compatibility, it works on all existing computer and telephone systems, with or without NFC.

How to Prevent Stalkerware from Infecting Your Phone

To prevent stalkerware from infecting your phone, you can follow these steps:

  • Be cautious about who has access to your phone: Don’t let people borrow your phone or have physical access to it if you don’t trust them.
  • Use strong passwords and security settings: Use a strong password, PIN, or biometric authentication to lock your phone and enable features like Find My Device or Find My iPhone in case your phone is lost or stolen.
  • Be careful what you click on: Be cautious of links or attachments that come from unknown or suspicious sources. Only download apps or files from trusted or official sources.
  • Keep your phone and apps updated: Make sure your phone’s operating system and apps are up to date with the latest security patches. These updates often include fixes for vulnerabilities that could be exploited by stalkerware or other malware.
  • Install a reputable antivirus or security app: Antivirus and security apps can help to protect your phone from stalkerware and other types of malware.

Consequently, following these steps helps protect against stalkerware.

If you suspect that you may have stalkerware installed on your device, look for these signs:

  • Sudden battery drain or overheating
  • Device turning on or off by itself or behaving strangely
  • Unusual spikes in data usage or unexpected charges on your phone bill
  • Unrecognized apps or files appearing on your device
  • Strange or unwanted messages, calls, or emails from unknown numbers or addresses
  • A sense that someone knows too much about your activities, location, or conversations

Detecting and Eliminating Stalkerware

Suspecting stalkerware’s presence calls for swift action to safeguard your privacy and security. Implement these steps:

  • Rely on Reputable Antivirus or Security Apps: Utilize antivirus or security apps like Malwarebytes, Kaspersky Internet Security, or Avast Mobile Security to detect and remove stalkerware.

  • Unmask Anomalous Apps or Files: If unfamiliar apps or files appear, suspect stalkerware’s presence. Scrutinize permissions for unrecognizable apps and uninstall those deemed suspicious.

  • Monitor Phone Bill for Unusual Activity: Detecting spikes in data usage or unexpected charges on your phone bill might indicate stalkerware. Investigate with your phone carrier.

  • Practice Caution with Clicks: Avoid clicking on links or opening attachments from unknown senders, as these might harbor stalkerware.

  • Stay Updated: Regularly update your device’s operating system and apps. Updates often include security patches that shield you from stalkerware.

  • Empower Yourself and Others: Educate yourself about stalkerware

Prevention is Crucial

To safeguard against stalkerware, focus on prevention. Here are some key tips:

  • Be cautious about who has access to your device: Don’t let people borrow your device or have physical access to it if you don’t trust them.
  • Use strong passwords and security settings: Use a strong password, PIN, or biometric authentication to lock your device and enable features like Find My Device or Find My iPhone in case your device is lost or stolen.
  • Be careful what you click on: Be cautious of links or attachments that come from unknown or suspicious sources. Only download apps or files from trusted or official sources.
  • Keep your device and apps updated: Make sure your device and all of your apps are up to date with the latest security patches and updates. This will help to protect against vulnerabilities that could be exploited by stalkerware or other malware.
  • Install a reputable antivirus or security app: Antivirus and security apps can help to detect and remove stalkerware, as well as protect you from other types of malware.

Resources for Stalkerware Victims

  • The Coalition Against Stalkerware: https://stopstalkerware.org/: The Coalition Against Stalkerware is an international organization that works to combat stalkerware. The coalition provides resources for victims of stalkerware, as well as advocates for stronger laws and regulations to protect people from stalkerware.
  • The National Network to End Domestic Violence: https://www.thehotline.org/: The National Network to End Domestic Violence is a US-based organization that provides resources for victims of domestic violence, including information on stalkerware. The organization also has a hotline that victims can call for support.
  • The Cyber Civil Rights Initiative: https://cybercivilrights.org/: The Cyber Civil Rights Initiative is a US-based organization that works to protect people from online abuse, including stalkerware. The organization provides resources for victims of online abuse, as well as advocates for stronger laws and regulations to protect people from online abuse.

Latest Research

In recent years, researchers have discovered several new methods for using stalkerware. For example, a new variant of stalkerware called Cerberus is capable of infecting devices over Bluetooth. Cerberus can then be used to track the victim’s location, record their calls and conversations, and even take photos and videos of them without their knowledge.

New Laws and Regulations

Subsequently, governments worldwide are enacting new laws. For example, the European Union has adopted a new directive that criminalizes the use of stalkerware in the EU. The United States has also taken steps to combat stalkerware, such as creating a new task force to investigate the use of stalkerware.

New Resources Available for Stalkerware Victims

In addition to the steps you can take to protect yourself from stalkerware, there are also a number of resources available to help victims of stalkerware. These resources offer support, advice, and legal assistance.

Stalkerware Survivors Share Stories of Trauma and Resilience

Sarah, a victim of stalking by her ex-boyfriend, shares her story:

I discovered the stalkerware only after noticing unusual patterns like battery drain and phone restarts. My ex-boyfriend was tracking my location, reading my messages, and even listening to my phone calls, causing me fear and distress. After reporting the stalkerware to the company’s IT department, they removed it and took action against my former partner.

John, a victim of workplace surveillance, reveals his experience:

My boss installed stalkerware to monitor my work hours, emails, and phone calls, making me feel controlled and distrustful. Discovering the stalkerware led me to report it to the company’s IT department, which removed it and disciplined my boss. While still employed, I’m now more cautious about who I trust.

Maria, a victim of government surveillance, describes her ordeal:

Similarly, the government tracked my activities using stalkerware.Seeking help from a human rights organization, I filed a complaint, received legal assistance, and had the stalkerware removed. Continuing my fight for justice, I’m now empowered to speak up.

How to Protect Yourself from Stalkerware: A Summary

Stalkerware is a serious threat to privacy and safety. By being aware of the risks and taking steps to protect yourself, you can help to prevent yourself from becoming a victim.

Here are some additional tips to help you stay safe from stalkerware:

  • Be aware of the latest stalkerware trends: Stalkerware developers are constantly finding new ways to infect devices. It’s important to stay up-to-date on the latest trends so that you can protect yourself.
  • Talk to your friends and family about stalkerware: The more people who are aware of the risks, the less likely it is that you will become a victim.
  • Support legislation to combat stalkerware: There are a number of laws and regulations being proposed to combat stalkerware. By supporting these laws, you can help make using stalkerware more difficult.

Follow these guidelines to effectively protect yourself from stalkerware and potential harm.

Human Limitations in Strong Passwords Creation

Digital image showing a confused user at a computer surrounded by complex password symbols

How to Create Strong Passwords Despite Human Limitations

Human Limitations in Strong Passwords are crucial in safeguarding our personal and professional data online. But do you know how to craft a robust password capable of thwarting hacking attempts? In this article, we delve into the impact of human factors on password security. Furthermore, you will gain insights on overcoming these limitations and creating formidable passwords.

For comprehensive threat assessments and innovative solutions, delve into “Human Limitations in Strong Passwords.” Stay informed by exploring our constantly updated topics..

[bws_pdfprint display=’print’]Human Limitations in Strong Passwords,” authored by Jacques Gascuel, the visionary behind cutting-edge sensitive data security and safety systems, offers invaluable insights into the field of human-created password security. Are you ready to improve your understanding of password protection?

Human Limitations in Strong Passwords: Cybersecurity’s Weak Link

Passwords are essential for protecting our data on the Internet. But creating a strong password is not easy. It requires a balance between security and usability. In this article, we will explain what entropy is and how it measures the strength of a password. We will also explore the limitations and problems associated with human password creation. We will show that these factors reduce entropy and password security, exposing users to cyber attacks. We will also provide some strategies and tips to help users create stronger passwords.

What is Entropy and How Does it Measure Password Strength?

Entropy is a concept borrowed from information theory. It measures the unpredictability and randomness of a system. The higher the entropy, the more disordered the system is, and the harder it is to predict.

In the context of passwords, entropy measures how many attempts it would take to guess a password through brute force. In other words, entropy measures the difficulty of cracking a password. The higher the entropy, the stronger the password is, and the harder it is to crack.

However, entropy is not a fixed value, but a relative measure that depends on various factors, such as the length, composition, frequency, and popularity of the password. We will explain these factors in more detail later.

How Do Cognitive Biases Influence Password Creation?

Cognitive Biases in Password Creation

Cognitive biases, such as confirmation bias and anchoring bias, significantly influence how users create passwords. Understanding “Human Limitations in Strong Passwords” is essential to recognize and overcome these biases for better password security.

Cognitive biases are reasoning or judgment errors that affect how humans perceive and process information. They are often the result of heuristics, mental shortcuts used to simplify decision-making. These biases can have adaptive advantages but also lead to errors or distortions of reality.

In password creation, cognitive biases can influence user choices, leading to passwords that make sense to them, linked to their personal life, culture, environment, etc. These passwords are often predictable, following logical or mnemonic patterns, reducing entropy.

For example, humans are subject to confirmation bias, thinking their password is strong enough because it meets basic criteria like length or composition, without considering other factors like character frequency or diversity.

They are also prone to anchoring bias, choosing passwords based on personal information like names, birthdates, pets, etc., not realizing this information is easily accessible or guessable by hackers.

Availability bias leads to underestimating cyber attack risks because they haven’t been victims or witnesses of hacking, or they think their data isn’t interesting to hackers.

Human Factors in Strong Password Development: Cognitive Biases

Strategies to Overcome Cognitive Biases

To mitigate the impact of cognitive biases, consider adopting better password practices:

  • Utilize a different password for each service, especially for sensitive or critical accounts, such as email, banking, or social media.
  • Employ a password manager, which is a software or application that securely stores and generates passwords for each service. Password managers can assist users in creating and recalling strong, random passwords, all while maintaining security and convenience.
  • Implement two-factor authentication, a security feature that necessitates users to provide an additional verification method, such as a code sent to their phone or email, or a biometric scan, in order to access their accounts. Two-factor authentication can effectively thwart hackers from gaining access to accounts, even if they possess the password.
  • Regularly update passwords, but refrain from doing so excessively, in order to prevent compromise by hackers or data breaches. Users should change their passwords when they suspect or confirm a breach or when they detect suspicious activity on their accounts. It’s also advisable for users to avoid changing their passwords too frequently, as this can lead to weaker passwords or password reuse.

Addressing Human Challenges in Secure Password Creation with Freemindtronic’s Advanced Technologies

Understanding Human Constraints in Robust Password Generation

The process of creating strong passwords often clashes with human limitations. Freemindtronic’s EviPass NFC HSM and EviPass HSM PGP technologies, integral to the PassCypher range, acknowledge these human factors in strong password development. By automating the creation process and utilizing Shannon’s entropy model, these technologies effectively mitigate the cognitive biases that typically hinder the creation of secure passwords.

Password Security and the Fight Against Cyber Attacks

In the context of increasing cyber threats, the security of passwords becomes paramount. Freemindtronic’s solutions offer a robust defense against cyber attacks by generating passwords that exceed conventional security standards. This approach not only addresses the human challenges in creating strong passwords but also fortifies the digital identity protection of users.

Leveraging Entropy in Passwords for Enhanced Security

The concept of entropy in passwords is central to Freemindtronic’s technology. By harnessing advanced entropy models, these systems ensure a high level of randomness and complexity in password creation, significantly elevating password security. This technical sophistication is crucial in overcoming human limitations in generating secure passwords.

Cognitive Biases in Passwords: Simplifying User Experience

Freemindtronic’s technologies also focus on the human aspect of password usage. By reducing the cognitive load through features like auto-fill and passwordless access, these systems address common cognitive biases. This user-friendly approach not only enhances the ease of use but also contributes to the overall strategy for strong password management.

Adopting Strong Password Strategies for Digital Identity Protection

Incorporating strong password strategies is essential in safeguarding digital identities. Freemindtronic’s technologies empower users to adopt robust password practices effortlessly, thereby enhancing digital identity protection. This is achieved through the generation of complex passwords and the elimination of the need for manual password management.

Elevating Password Security in the Digital Age

Freemindtronic’s EviPass NFC HSM and EviPass HSM PGP technologies are at the forefront of addressing human limitations in strong password creation. By integrating advanced entropy in passwords, focusing on user-centric design, and combating the risks of cyber attacks, these technologies are setting new benchmarks in password security and digital identity protection. Their innovative approach not only acknowledges but also effectively overcomes the human challenges in secure password creation, marking a significant advancement in the field of digital security.

Human Constraints in Robust Password Generation

There are various methods to help users create strong, memorable passwords. These methods have pros and cons, which should be understood to choose the most suitable for one’s needs.

Mnemonic Passwords: Balancing Memory and Security

Mnemonic passwords are based on phrases or acronyms, serving as memory aids. For example, using the phrase “I was born in 1984 in Paris” to create the password “Iwbi1984iP”.

Advantages of mnemonic passwords:

  • Easier to remember than random passwords, using semantic memory, more effective than visual or auditory memory.
  • Can be longer than random passwords, composed of multiple words or syllables, increasing entropy.

Disadvantages of mnemonic passwords:

  • Often predictable, following logical or grammatical patterns, reducing entropy.
  • Vulnerable to dictionary attacks, containing common words or personal information, easily accessible or guessable by hackers.
  • Difficult to type, containing special characters like accents or spaces, not always available on keyboards.

The Trade-Off Between Mnemonics and Entropy

To balance memory and security, users should use mnemonics that are not too obvious or common, but rather personal and unique. They should also avoid using the same mnemonic for different passwords, or using slight variations of the same mnemonic. They should also add some randomness or complexity to their mnemonics, such as numbers, symbols, or capitalization.

Random Passwords: Entropy and Ease of Use

Random passwords are composed of randomly chosen characters, without logic or meaning. For example, the password “qW7x#4Rt”.

Advantages of random passwords:

  • Harder to guess than mnemonic passwords, not following predictable patterns, increasing entropy.
  • More resistant to dictionary attacks, not containing common words or personal information.

Disadvantages of random passwords:

  • Harder to remember than mnemonic passwords, not using semantic memory.
  • Can be shorter than mnemonic passwords, composed of individual characters, reducing entropy.

Phrase-Based Passwords: Entropy and Ease of Use

Phrase-based passwords are composed of several words forming a phrase or expression. For example, the password “The cat sleeps on the couch”.

Advantages of phrase-based passwords:

  • Easier to remember than random passwords, using semantic memory.
  • Can be longer than random passwords, composed of multiple words, increasing entropy.

Disadvantages of phrase-based passwords:

  • Often predictable, following logical or grammatical patterns, reducing entropy.
  • Vulnerable to dictionary attacks, containing common words or expressions.
  • Difficult to type, containing spaces, not always accepted by online services.

Evaluating Phrase-Based Password Effectiveness

To evaluate the effectiveness of phrase-based passwords, users should consider the following criteria:

  • Phrase length plays a crucial role: Longer phrases tend to result in higher entropy. However, it’s important to strike a balance, as excessively long phrases can become challenging to type or recall.
  • The diversity of words also matters: Greater word diversity contributes to higher entropy. Nevertheless, it’s essential to avoid overly obscure words, as they might prove difficult to remember or spell.
  • Randomness in word selection boosts entropy: The more random the words, the greater the entropy. Yet, it’s necessary to maintain some level of coherence between words, as entirely unrelated words can pose memory and association challenges.

Human-Generated Random Passwords: Entropy and Ease of Use

Human-generated random passwords are composed of randomly chosen characters by the user, without logic or meaning. For example, the password “qW7x#4Rt”.

Advantages :

  • Harder to guess than mnemonic or phrase-based passwords, increasing entropy.
  • More resistant to dictionary attacks, not containing common words or personal information.

Disadvantages:

  • Harder to remember than mnemonic or phrase-based passwords.
  • Often biased by user preferences or habits, favoring certain characters or keyboard positions, reducing entropy.

The Risks of Low Entropy in Human-Created Passwords

Low entropy passwords have significant consequences on the security of personal and professional data. Weak passwords are more vulnerable to cyber attacks, especially brute force. Hackers can use powerful software or machines to test billions of combinations per second. Once the password is found, they can access user accounts, steal data, impersonate, or spread viruses or spam.

Consequences of Predictable Passwords on Cybersecurity

The consequences of predictable passwords on cybersecurity are:

  • Data breach: Hackers can access user data, such as personal information, financial records, health records, etc. They can use this data for identity theft, fraud, blackmail, or sell it to third parties.
  • Account takeover: Hackers can access user accounts, such as email, social media, online shopping, etc. They can use these accounts to impersonate users, send spam, make purchases, or spread malware.
  • Reputation damage: Hackers can access user accounts, such as professional or academic platforms, etc. They can use these accounts to damage user reputation, post false or harmful information, or sabotage user work or research.

Understanding the Vulnerability of Low Entropy Passwords

Password Length and Entropy

The vulnerability of passwords depends on various factors, including the length, composition, frequency, and popularity of the password. Understanding “Human Limitations in Strong Passwords” is crucial for safeguarding your online data. Longer and more complex passwords offer higher entropy and are harder to crack.

Composition Complexity

Complex passwords that include a variety of character types, such as lowercase, uppercase, numbers, and symbols, significantly enhance security. This aspect of “Human Limitations in Strong Passwords” is often overlooked, but it’s essential for creating robust passwords.

Common vs. Rare Passwords

The frequency and popularity of passwords play a vital role in their vulnerability. Common passwords, like “123456” or “password,” are easily guessed, while rare and unique passwords, such as “qW7x#4Rt” or “The cat sleeps on the couch,” provide more security.

Password Composition

The composition of a password is a critical factor. Passwords based on common words or personal information are easier for hackers to guess. Understanding the impact of “Human Limitations in Strong Passwords” can help you make informed choices about password composition.

These factors collectively influence the time required for brute force attacks to uncover a password. Longer durations enhance password security, but it’s essential to consider the evolving computing power of hackers, which can reduce the time required to crack passwords over time and with advancing technology. Another factor that affects the vulnerability of passwords is their frequency and popularity.

Recurring Password Changes: A Challenge to Password Entropy

Another human limitation in creating strong passwords is the recurrent need to change them. Often mandated by online services for security, regular changes can paradoxically weaken password strength. This practice burdens users with remembering multiple passwords and inventing new ones frequently. It leads to slight modifications of existing passwords rather than generating new, more random ones. This habit reduces password entropy, making passwords more predictable and vulnerable to cyber attacks.

Impact of Frequent Password Updates on Security

Studies have shown that users required to change passwords every 90 days tend to create weaker, less diverse passwords. Conversely, those with less frequent changes generate more random and secure passwords. This illustrates the counterproductive nature of too-frequent mandatory password updates.

The Counterproductive Nature of Mandatory Password Changes

Mandatory password changes are often imposed by online services for security reasons. They aim to prevent password compromise by hackers or leaks. However, mandatory password changes can have negative effects on password security, such as:

  • Elevating cognitive load entails users remembering multiple passwords for each service and crafting new passwords whenever needed.
  • Dampening user motivation occurs when individuals view password changes as unnecessary or ineffective, leading to a neglect of password quality.
  • Diminishing password entropy arises when users opt for making slight modifications to old passwords rather than generating entirely new and random ones.

These effects negatively impact password security, making passwords more predictable and vulnerable to cyber attacks.

Research Insights on Low Entropy in Human Passwords

In this section, we will present some sources and findings from scientific studies conducted by researchers from around the world on passwords and entropy. We have verified the validity and accuracy of these sources using web search and citation verification tools. We have also respected the APA citation style.

Analyzing Global Studies on Password Security

Several studies have analyzed the security of passwords based on real databases of passwords disclosed following leaks or hacks. These studies have measured the entropy and the strength of passwords, as well as the patterns and the behaviors of users. Some of these studies are:

Key Findings from Password Entropy Research

Some of the key findings from these studies are:

  • any users maintain low-entropy passwords, relying on common words, personal information, or predictable patterns.
  • Furthermore, they tend to reuse passwords across multiple services, thereby elevating the risk of cross-service compromise.
  • In addition, they typically refrain from changing passwords regularly, unless prompted to do so by online services or following a security breach.
  • Surprisingly, a significant portion of users remains unaware of the critical importance of password security or tends to overestimate the strength of their passwords.
  • Moreover, a considerable number of users exhibit reluctance towards the adoption of password managers or two-factor authentication, often citing usability or trust concerns.

These findings confirm the low entropy of human passwords, and the need for better password practices and education.

Password Reuse and Its Impact on Entropy

Another issue with human password creation is password reuse, a common practice among Internet users, who have to remember multiple passwords for different services. Password reuse consists of using the same or similar passwords for different accounts, such as email, social media, online shopping, etc. Password reuse can reduce the cognitive load and the effort required to create and remember passwords, but it also reduces the entropy and the security of passwords.

The Risks Associated with Password Reuse

The risks associated with password reuse are:

  • Cross-service compromise: If a password is discovered or compromised on one service, it can be used to access other services that use the same or similar password. For example, if a hacker obtains a user’s email password, they can use it to access their social media, online shopping, or banking accounts, if they use the same password or a slight variation of it.
  • Credential stuffing: Credential stuffing is a type of cyberattack that uses automated tools to test stolen or leaked usernames and passwords on multiple services. For example, if a hacker obtains a list of usernames and passwords from a data breach, they can use it to try to log in to other services, hoping that some users have reused their passwords.
  • Password cracking: Password cracking is a type of cyberattack that uses brute force or dictionary methods to guess passwords. For example, if a hacker obtains a user’s password hash, they can use it to try to find the plain text password, using lists of common or leaked passwords.

These risks show that password reuse can expose users to cyber threats, as a single password breach can compromise multiple accounts and data. Password reuse can also reduce the entropy of passwords, as users tend to use common or simple passwords that are easy to remember and type, but also easy to guess or crack.

Addressing the Security Flaws of Reusing Passwords

To mitigate the security vulnerabilities associated with password reuse, users should embrace improved practices for password creation and management. Some of these recommended practices include:

  • Utilize distinct passwords for each service, particularly for sensitive or crucial accounts such as email, banking, or social media. This approach ensures that if one password is compromised, it won’t jeopardize other accounts or data.
  • Employ a password manager, which is software or an application designed to securely store and generate passwords for each service. Password managers assist users in crafting and recalling strong, randomly generated passwords, all while upholding security and convenience. Additionally, these tools can notify users about password breaches or weak passwords, as well as suggest password changes or updates.
  • Implement two-factor authentication (2FA), a security feature demanding users to provide an additional verification method, such as a code sent to their phone or email, or a biometric scan. This extra layer of security thwarts hackers from gaining access to accounts solely through knowledge of the password, as they would require the second factor as well.
  • Adopt a regular password change strategy, though not excessively frequent, to preempt compromise by hackers or data leaks. Passwords should be modified when users suspect or verify a breach, or when they detect suspicious activity on their accounts. It’s also advisable to avoid changing passwords too frequently, as this can potentially result in weaker passwords or password reuse.

These practices can help users avoid password reuse and increase the entropy and security of their passwords. They can also reduce the cognitive load and the effort required to create and remember passwords, by using tools and features that simplify password creation and management.

Behavioral Resistance in Secure Password Practices

Another issue with human password creation is resistance to behavioral changes, a psychological phenomenon preventing users from adopting new habits or modifying old ones regarding passwords. Users are often reluctant to change passwords, even when aware of risks or encouraged to do so. This resistance can be due to factors like laziness, ignorance, confidence, fear, satisfaction, etc.

Overcoming Psychological Barriers in Password Security

Psychological barriers can hinder password security, as users may not follow the best practices or recommendations to create stronger passwords. To overcome these barriers, users need to be aware of the importance and benefits of password security, as well as the costs and risks of password insecurity. Some of the ways to overcome psychological barriers are:

  • Educating users about password security, explaining what entropy is, how it measures password strength, and how to increase it.
  • Motivating users to change passwords, providing incentives, feedback, or rewards for creating stronger passwords.
  • Persuading users to adopt password managers, demonstrating how they can simplify password creation and management, without compromising security or convenience.
  • Nudging users to use two-factor authentication, making it easy and accessible to enable and use this security feature.

Conclusion: Reinforcing Password Security Amidst Human Limitations

In this article, we have explained what entropy is and how it measures the strength of a password. We also explored the limitations and problems associated with human password creation, such as cognitive biases, human generation methods, password reuse, and resistance to behavioral changes. We have shown that these factors reduce entropy and password security, exposing users to cyber attacks. We have also provided some strategies and tips to help users create stronger passwords.

We hope this article has helped you understand the importance of password security and improve your password practices. Remember, passwords protect your digital identity and data online. Creating strong passwords is not only a matter of security, but also of responsibility.

Terrapin attack: How to Protect Yourself from this New Threat to SSH Security

SSH handshake with Terrapin attack and EviKey NFC HSM

Terrapin Attack: How to Protect Your SSH Security

The Terrapin attack is a serious vulnerability in the SSH protocol that can be used to downgrade the security of your SSH connections. This can allow attackers to gain access to your sensitive data. In this article, we will explain what the Terrapin attack is, how it works, and how you can protect yourself from it.

Terrapin attack: CVE-2023-48795 SSH security vulnerability articles for in-depth threat reviews and solutions. Stay informed by clicking on our scrolling topics.

[bws_pdfprint display=’print’]Shield Your SSH Security from the Sneaky Terrapin Attack written by Jacques Gascuel, inventor of sensitive data safety and security systems. Are you safeguarding your SSH connections? Stay vigilant against the Terrapin attack, a stealthy vulnerability that can compromise your SSH security and expose your sensitive data.

Protect Yourself from the Terrapin Attack: Shield Your SSH Security with Proven Strategies

SSH is a widely used protocol for secure communication over the internet. It allows you to remotely access and control servers, transfer files, and encrypt data. However, SSH is not immune to attacks, and a recent vulnerability OpenSSH before 9.6 (CVE-2023-48795) has exposed a serious flaw in the protocol itself. This flaw, dubbed the Terrapin attack, can downgrade the security of SSH connections by truncating cryptographic information. In this article, we will explain what the Terrapin attack is, how it works, and how you can protect yourself from it.

Why you should care about the Terrapin attack

The Terrapin attack is not just a theoretical threat. It is a real and dangerous attack that can compromise the security of your SSH connections and expose your sensitive data. The consequences of a successful Terrapin attack can be severe, such as:

  • Data breaches: The attacker can access your confidential information, such as passwords, keys, files, or commands, and use them for malicious purposes.
  • Financial losses: The attacker can cause damage to your systems, services, or assets, and demand ransom or extort money from you.
  • Reputation damage: The attacker can leak your data to the public or to your competitors, and harm your credibility or trustworthiness.

Therefore, it is important to be aware of the Terrapin attack and take the necessary measures to prevent it. In the following sections, we will show you how the Terrapin attack works, how to protect yourself from it, and how to use PassCypher HSM PGP and EviKey NFC HSM to enhance the security of your SSH keys.

A prefix truncation attack on the SSH protocol

The Terrapin attack is a prefix truncation attack that targets the SSH protocol. It exploits a deficiency in the protocol specification, namely not resetting sequence numbers and not authenticating certain parts of the handshake transcript. By carefully adjusting the sequence numbers during the handshake, an attacker can remove an arbitrary amount of messages sent by the client or server at the beginning of the secure channel without the client or server noticing it.

This manipulation allows the attacker to perform several malicious actions, such as:

  • Downgrade the connection’s security by forcing it to use less secure client authentication algorithms
  • Bypass the keystroke timing obfuscation feature in OpenSSH, which may allow the attacker to brute-force SSH passwords by inspecting the network packets
  • Exploit vulnerabilities in SSH implementations, such as AsyncSSH, which may allow the attacker to sign a victim’s client into another account without the victim noticing

To pull off a Terrapin attack, the attacker must already be able to intercept and modify the data sent from the client or server to the remote peer. This makes the attack more feasible to be performed on the local network.

Unveiling the SSH Handshake: Exposing the Terrapin Attack’s Weakness

The SSH Handshake Process

The SSH handshake is a crucial process that establishes a secure channel between a client and server. It consists of the following steps:

  1. TCP connection establishment: The client initiates a TCP connection to the server.
  2. Protocol version exchange: The client and server exchange their protocol versions and agree on a common one. Then, the algorithm negotiation takes place.
  3. Algorithm negotiation: The client and server exchange lists of supported algorithms for key exchange, encryption, MAC, and compression. Then, they select the first matching algorithm.
  4. Key exchange: The client and server use the agreed-upon key exchange algorithm to generate a shared secret key. They also exchange and verify each other’s public keys. Then, the service request is sent.
  5. Service request: The client requests a service from the server, such as ssh-userauth or ssh-connection. Then, the client authenticates itself to the server using a supported method, such as password, public key, or keyboard-interactive.
  6. User authentication: The client authenticates itself to the server using a supported method, such as password, public key, or keyboard-interactive. Then, the channel request is sent.
  7. Channel request: The client requests a channel from the server, such as a shell, a command, or a subsystem. Thus, encrypted communication is enabled.

The Terrapin Attack

The Terrapin attack exploits a vulnerability in the SSH handshake by manipulating the sequence numbers and removing specific messages without compromising the secure channel integrity. This stealthy attack is difficult to detect because it doesn’t alter the overall structure or cryptographic integrity of the handshake.

For example, the attacker can eliminate the service request message sent by the client, which contains the list of supported client authentication methods. This forces the server to resort to the default method, typically password-based authentication. The attacker can then employ keystroke timing analysis to crack the password.

Alternatively, the attacker can target the algorithm negotiation message sent by the server, which lists the supported server authentication algorithms. By removing this message, the attacker forces the client to use the default algorithm, usually ssh-rsa. This opens the door for the attacker to forge a fake public key for the server and deceive the client into accepting it.

To illustrate the process of a Terrapin attack, we have created the following diagram:

Hackers exploit OAuth2 flaw to bypass 2FA on google accounts google account security flaw

As you can see, the diagram shows the steps from the interception of the communication by the attacker to the injection of malicious packets. It also highlights the stealthiness and the difficulty of detection of the attack.

Summery

The Terrapin attack is a serious threat to SSH security. By understanding how it works, you can take steps to protect yourself from it. Here are some tips:

  1. Make sure your SSH server is up to date with the latest security patches.
  2. Use strong passwords or public key authentication.
  3. Enable SSH key fingerprint verification.

How to protect yourself from the Terrapin attack: Best practices and tools

The Terrapin attack is a serious threat to SSH security, and it affects many SSH client and server implementations, such as OpenSSH, PuTTY, FileZilla, and more. Here are some steps you can take to protect yourself from it:

  • Update your SSH client and server to the latest versions. Many vendors have released patches that fix the vulnerability or introduce a strict key exchange option that prevents the attack. You can check if your SSH software is vulnerable by using the Terrapin vulnerability scanner.
  • Use strong passwords and public key authentication. Avoid using weak or default passwords that can be easily guessed by the attacker. Use public key authentication instead of password authentication, and make sure your public keys are verified and trusted.
  • Use secure encryption modes. Avoid using vulnerable encryption modes, such as ChaCha20-Poly1305 or AES-CBC with default MACs. Use encryption modes that use authenticated encryption with associated data (AEAD), such as AES-GCM or Chacha20-Poly1305@openssh.com.
  • Use a VPN or a firewall. If possible, use a VPN or a firewall to encrypt and protect your SSH traffic from being intercepted and modified by the attacker. This will also prevent the attacker from performing other types of attacks, such as DNS spoofing or TCP hijacking.
  • Implement a strict security policy on your local networks. Limit the access to your SSH servers to authorized users and devices, and monitor the network activity for any anomalies or intrusions.

How to use PassCypher HSM PGP and EviKey NFC HSM to protect your SSH keys: A secure and convenient solution

A good way to enhance the security of your SSH keys is to use PassCypher HSM PGP and EviKey NFC HSM. These are products from PassCypher), a company specialized in data security. They offer a secure and convenient solution for generating and storing your SSH keys.

PassCypher HSM PGP is a system that embeds a SSH key generator, allowing you to choose the type of algorithm – RSA (2048, 3072, 4096) or ECDSA (256,384, 521), and ED25519. The private key is generated and stored in a secure location, making it inaccessible to attackers.

EviKey NFC HSM is a contactless USB drive that integrates with PassCypher HSM PGP. It provides an additional layer of security and convenience for users who can easily unlock their private SSH key with their smartphone.

To show how PassCypher HSM PGP and EviKey NFC HSM can protect your SSH keys from the Terrapin attack, we have created the following diagram:

SSH handshake process with Terrapin attack illustration
This image illustrates the Terrapin attack, a stealthy attack that exploits a vulnerability in the SSH handshake. The attacker can manipulate the sequence numbers and remove specific messages without compromising the secure channel integrity. This can lead to a variety of security risks, including password cracking and man-in-the-middle attacks.

As you can see, the diagram shows how this solution effectively protects your SSH keys from the Terrapin attack. It also shows the benefits of using a contactless USB drive, such as:

  • Enhanced security: The private key is physically externalized and protected with a contactless authentication mechanism.
  • Convenience: Easy unlocking with a smartphone.
  • Ease of use: No additional software required.
  • Industrial-grade security: Equivalent to SL4 according to the standard IEC 62443-3-3.

Safeguarding Your SSH Keys with a Contactless USB Drive: A Comprehensive Guide

If you’re seeking a comprehensive guide to securely store your SSH keys using a contactless USB drive, look no further than this detailed resource: [Link to the article ([https://freemindtronic.com/how-to-create-an-ssh-key-and-use-a-nfc-hsm-usb-drive-to-store-it-securely/])]

This guide meticulously walks you through the process of:

  1. Generating an SSH key pair leveraging PassCypher HSM PGP
  2. Protecting the private SSH key within the EviKey NFC HSM USB drive
  3. Unlocking the private SSH key employing your smartphone
  4. Establishing a secure connection to an SSH server using the EviKey NFC HSM USB drive

Alongside step-by-step instructions, the guide also includes illustrative screenshots. By adhering to these guidelines, you’ll effectively safeguard and conveniently manage your SSH keys using a contactless USB drive.

Statistics on the Terrapin attack: Facts and figures

Statistics on the Terrapin attack: Facts and figures

The Terrapin attack is a serious cybersecurity threat that affects SSH connections. We have collected some statistics from various sources to show you the scale and impact of this attack. Here are some key facts and figures:

  • The Shadowserver Foundation reports that nearly 11 million SSH servers exposed on the internet are vulnerable to the Terrapin attack. This is about 52% of all IPv4 and IPv6 addresses scanned by their monitoring system.
  • The most affected countries are the United States (3.3 million), China (1.3 million), Germany (1 million), Russia (704,000), Singapore (392,000), Japan (383,000), and France (379,000).
  • The Terrapin attack affects many SSH client and server implementations, such as OpenSSH, PuTTY, FileZilla, Dropbear, libssh, and more. You can see the complete list of known affected implementations here).
  • You can prevent the Terrapin attack by updating your SSH software to the latest version, using secure encryption modes, and enabling strict key exchange. You can also use the Terrapin vulnerability scanner, available on GitHub, to check your SSH client or server for vulnerability.
  • A team of researchers from the Horst Görtz Institute for IT Security at Ruhr University Bochum in Germany discovered and disclosed the Terrapin attack. They published a detailed paper and a website with the technical details and the implications of the attack. Conclusion: How to stay safe from the Terrapin attack

The Terrapin attack is a serious threat to SSH security. It lets hackers break into SSH servers by exploiting a vulnerability in the protocol. To protect yourself effectively, you need to do the following:

  • Update your SSH software to the latest version
  • Use two-factor authentication
  • Store your SSH keys securely
  • Use PassCypher HSM PGP and EviKey NFC HSM

Conclusion: How to stay safe from the Terrapin attack

The Terrapin attack is a serious threat to SSH security. It allows hackers to break into SSH servers by exploiting a vulnerability in the protocol. To protect yourself effectively, you need to update your SSH software, use two-factor authentication, store your SSH keys securely, and use PassCypher HSM PGP and EviKey NFC HSM. If you found this article useful, please feel free to share it with your contacts or leave us a comment.